Hello, you are using an old browser that's unsafe and no longer supported. Please consider updating your browser to a newer version, or downloading a modern browser.

Free Practice Test

Free CRISC Practice Test

Check your readiness for the ISACA Certified in Risk and Information Systems Control (CRISC) exam with 50 risk-practitioner questions across all four domains of the 2025 exam content outline, each with an instant explanation. Free to take, timed to the pace of the real exam, and retake it as often as you want.

50Questions, or a 25-question quick test
80 minTimer, paced like the real exam
4CRISC domains covered
A–DEvery answer choice explained, right and wrong

Try a question before you start

Pick an answer to see the reasoning. These are samples from the 50-question bank; the full test starts below.

Governance

A regional bank hires its first dedicated IT risk practitioner. The board asks for a report on the top IT risks within a month, but the enterprise has never defined how much risk it is willing to accept. What should the practitioner do FIRST?

Why not A? Scan results are technical findings, not risk. Without a statement of appetite there is no basis for saying which findings matter to the board.

Why not C? A framework organizes the work but cannot tell you how much risk this bank tolerates; that is a management decision the framework expects as an input.

Why not D? An inventory of issues is useful later, but it produces a list of problems ranked by whoever is loudest rather than by impact on business objectives.

B is correct. Risk appetite is the amount of risk the enterprise is willing to accept in pursuit of its objectives, and it is the reference point every later rating, prioritization and treatment decision depends on. Establishing it with senior management comes before reporting on any individual risk.

Risk Assessment

A risk practitioner at an online travel agency is developing risk scenarios for the booking platform. A workshop produces a long list of technical failure modes suggested by engineers. To make the scenarios useful for risk analysis, what is the MOST important element to include in each one?

Why not A? Vendor names help with treatment later, but a scenario built around a vendor rather than an outcome tells the business nothing about what is at stake.

Why not B? A severity score describes a vulnerability, not a scenario. Many scenarios involve no single vulnerability at all, such as a key person leaving or a supplier failing.

Why not C? Provenance is useful metadata for the register but does not make the scenario analyzable.

D is correct. A risk scenario describes a threat acting on an asset or process to produce a business consequence. Naming the affected asset and the consequence is what lets the scenario be rated for impact and likelihood and understood by the owner who must decide on it.

The full test has 50 questions like these. Start it now →

Start Your Free Practice Test

Enter your details, then choose a 25-question Quick Test or the full 50-question, 80-minute practice test.

First Name
Last Name
Phone

A Training Camp advisor may reach out about your results and study options. No spam, and you can opt out anytime.

Prefer to talk to someone?

What you get at the end

Your overall score, a score for each exam domain, and the domains to work on next.

Example report77%
Governance83%
Risk Assessment64%
Risk Response and Reporting78%
Technology and Security71%
Below 80% is flagged as an area to work on.

What's on the CRISC exam

4 weighted domains. The practice test draws questions from each in the same proportion.

  • 26%

    Governance

    Organizational and risk governance: strategy, culture, policies, ERM, lines of defense, appetite.

  • 22%

    Risk Assessment

    Risk events, threat modeling, vulnerabilities, scenarios, BIA, register, inherent and residual risk.

  • 32%

    Risk Response and Reporting

    Response options, control design and testing, KRIs and KCIs, monitoring, reporting to stakeholders.

  • 20%

    Technology and Security

    Enterprise architecture, operations, SDLC, projects, emerging tech, security concepts, privacy, DR.

Built on what our boot camp teaches

Every question maps to the same exam objectives we teach in the CRISC boot camp, and every answer choice has its own explanation, so a wrong answer still teaches you something. Questions last reviewed September 29, 2026.

  • Real exam: 150 questions in 4 hours.
  • To pass: a scaled score of 450 on a scale of 200 to 800.
  • This test: 50 questions on a 80-minute timer, or a 25-question quick test.
Read the full CRISC exam guide

This free ISACA CRISC practice test checks your readiness with 50 risk-practitioner questions across all four domains of the 2025 exam content outline, each with an explanation for every answer choice, under an 80-minute timer that matches the pace of the real exam. Built by Training Camp, an award-winning ISACA Elite+ Training Partner, and drawn from the same objectives we teach in our CRISC Certification Boot Camp.

What's on the ISACA Certified in Risk and Information Systems Control (CRISC) exam?

The CRISC exam is organized into four weighted domains under the exam content outline that took effect November 3, 2025: Governance (26%), Risk Assessment (22%), Risk Response and Reporting (32%), and Technology and Security (20%). This practice test draws its 50 questions from every domain in the same proportions: 13, 11, 16, and 10. For the full breakdown, see ISACA's official CRISC exam content outline.

The real exam has 150 multiple-choice questions and a 4-hour (240-minute) time limit, and it is scored on a scale of 200 to 800 with 450 required to pass. Questions are written from the IT risk practitioner's point of view: what should be done first, which input is most important, who owns the decision. The distractors are often sensible technical actions that skip a governance step or take a decision away from the risk owner, so practicing the practitioner's judgment matters more than memorizing control lists.

The 2025 outline kept the four-domain structure of the 2021 version but shortened two names: IT Risk Assessment became Risk Assessment, and Information Technology and Security became Technology and Security. Two percentage points moved from Technology and Security to Risk Assessment, and the topic list still names emerging technologies and the monitoring and reporting of emerging risks. Exams taken on or after November 3, 2025 use the 2025 outline, which this test follows.

How to use this practice test

Take it once under the 80-minute timer without notes. That works out to 1.6 minutes per question, the same pace as 150 questions in 4 hours on the real exam. Then read every explanation, including the ones for choices you did not pick. The wrong-answer explanations show the reasoning patterns ISACA expects, such as comparing residual risk with risk appetite before recommending a response, or escalating a risk acceptance to the owner instead of making it yourself. Use the per-domain breakdown to decide where to study, then retake the test after a week to see whether your judgment has shifted.

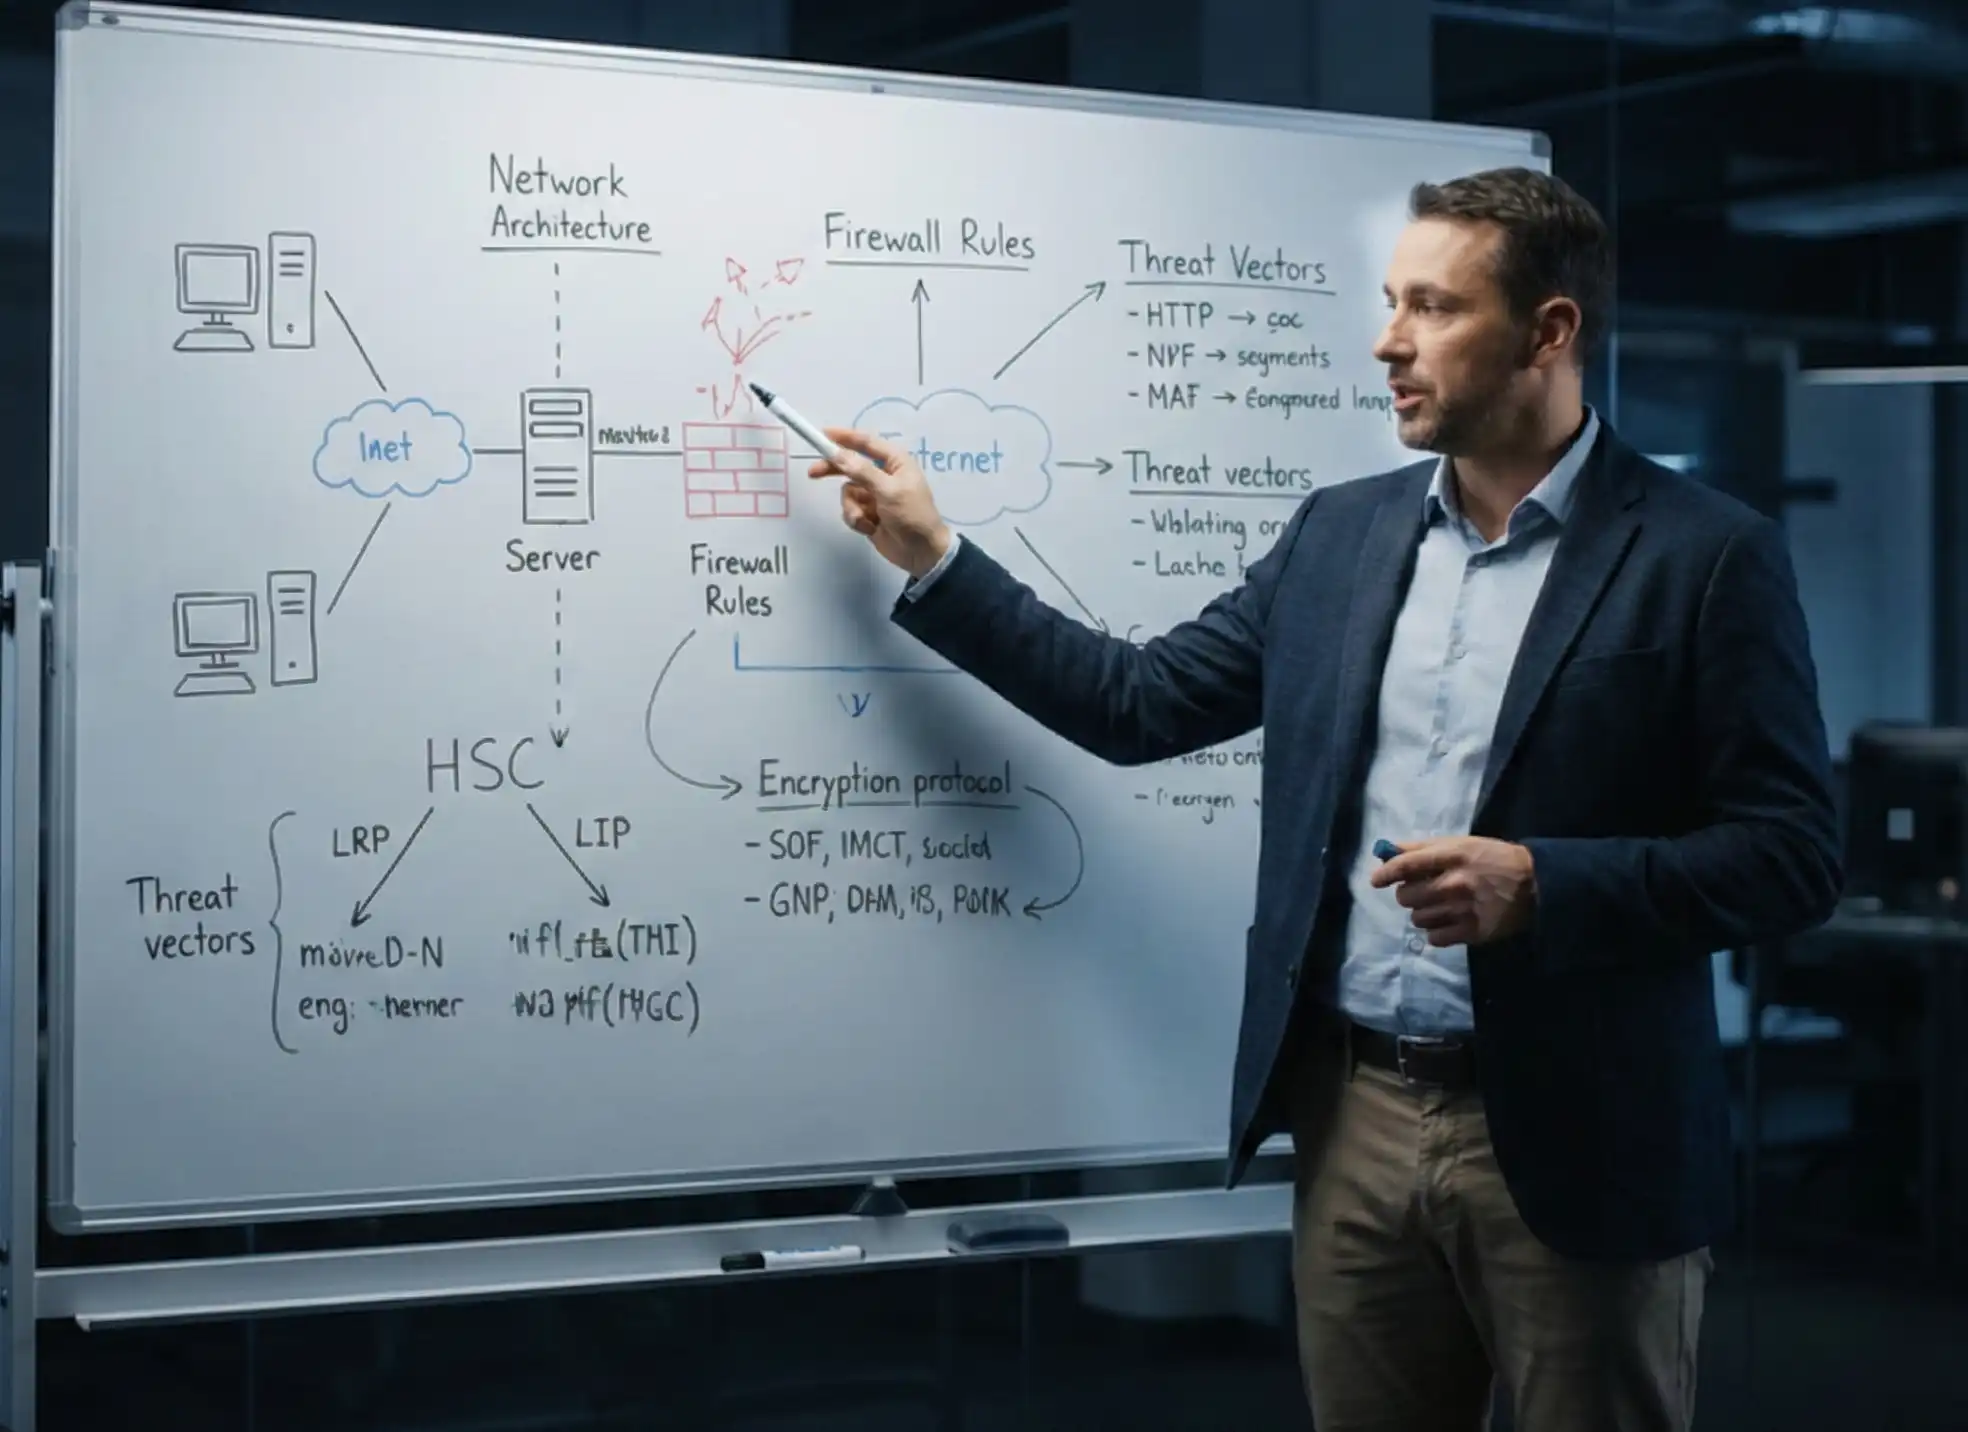
Training Camp instructor teaching network security at a whiteboard

How to get the most from it

Three steps, in this order.

Student working through practice questions at a laptop
Step 1

Take a baseline

Take the full test once without notes, so the score shows where you really stand.

Student reviewing material on a laptop
Step 2

Read every explanation

Including the ones you got right. The notes on the wrong choices explain the differences between similar concepts, like tokenization and encryption.

Students working on laptops in a Training Camp lab
Step 3

Fix one domain, then retake

Your results break down by domain. Study the weakest one for a week, then retake. Each Quick Test draws a fresh mix of questions.

CRISC Practice Test

Frequently Asked Questions

Quick answers about the test, the ISACA Certified in Risk and Information Systems Control (CRISC) exam, and how to prepare.

Is this CRISC practice test free?

Yes. All 50 questions are free to take, with a written explanation for every answer choice across all four ISACA CRISC domains, and you can retake it as often as you want.

How does this practice test work?

50 risk-practitioner questions drawn from all four CRISC domains, with an instant explanation after each answer and an 80-minute timer that matches the pace of the real exam (1.6 minutes per question). Your results break down by domain. It is a readiness check, not a substitute for full preparation.

How many questions are on the real CRISC exam?

The ISACA CRISC exam has 150 multiple-choice questions and a 4-hour (240-minute) time limit. Some items are unscored pretest questions, but you will not know which, so answer every question as if it counts.

What score do I need to pass CRISC?

CRISC is scored on a scale of 200 to 800, and you need a scaled score of 450 or higher to pass. The scaled score is not a percentage of questions answered correctly, and domain-level results are reported for information only.

What domains does the CRISC exam cover?

The exam content outline that took effect November 3, 2025 has four domains: Governance (26%), Risk Assessment (22%), Risk Response and Reporting (32%), and Technology and Security (20%). Compared with the 2021 outline, two domain names were shortened (IT Risk Assessment is now Risk Assessment, and Information Technology and Security is now Technology and Security) and two percentage points moved from Technology and Security to Risk Assessment.

What experience do I need to become CRISC certified?

You can sit the exam at any time, but to certify ISACA requires three or more years of cumulative work experience in IT risk management and information systems control, performing the tasks of a CRISC professional across at least two of the four domains. The experience must be gained within the ten years before you apply, ISACA offers no experience waivers or substitutions for CRISC, and you must apply within five years of passing the exam.

How hard is the CRISC exam?

CRISC tests judgment more than technical depth. Most questions describe a situation and ask what the risk practitioner should do first, which factor matters most, or who should make the decision, and several of the wrong choices are usually reasonable actions. Candidates who have worked in risk, audit, or security governance tend to find the reasoning familiar; others need to practice thinking in terms of risk owners, appetite and residual risk.

How should you prepare for the CRISC exam?

Study ISACA's official CRISC Review Manual and question database, learn the vocabulary of the exam content outline (risk appetite, KRIs, inherent versus residual risk, the three lines of defense), and consider an accelerated CRISC Certification Boot Camp that includes the exam voucher and a free retake if you need it.

Using your GI Bill®?

If you are a veteran or service member, your benefits can pay for CRISC prep.

  • Post-9/11 GI Bill®: our live online CRISC Certification Exam Preparatory Course is approved for Chapter 33 benefits, and the VA can reimburse the exam fee as well. See the GI Bill® prep course →
U.S. Army service member working on a laptop
Instructor-led Training Camp class

Ready to pass it for real?

The CRISC boot camp covers every exam domain with a live instructor, online or in person.

  • Exam voucher included
  • Free retake
  • 180 days of unlimited 1-on-1 coaching after class