Hello, you are using an old browser that's unsafe and no longer supported. Please consider updating your browser to a newer version, or downloading a modern browser.

Free Practice Test

Free CySA+ Practice Test
for CS0-004

Check your readiness for the CompTIA CySA+ CS0-004 exam with 50 exam-style questions across all four domains, each with an instant explanation. Free to take, with a 90-minute timer that matches the pace of the real exam, and retake it as often as you want.

50Questions, or a 25-question quick test
90 minTimer, paced like the real exam
4CS0-004 domains covered
A–DEvery answer choice explained, right and wrong

Try a question before you start

Pick an answer to see the reasoning. These are samples from the 50-question bank; the full test starts below.

Security Operations

A SOC analyst at a regional hospital is reconstructing a suspected credential theft. The SIEM shows the VPN concentrator recorded the attacker's login at 02:14, yet the domain controller logged the same account's Kerberos ticket request at 02:09, five minutes before the VPN session existed. Both timestamps were written by the devices themselves, both devices are healthy and neither log has gaps. What is the most likely cause?

Why not A? Log tampering is possible, but it is the least likely explanation for a clean five-minute offset with no gaps. Clock drift between devices produces exactly this kind of impossible ordering and should be ruled out first.

Why not B? Buffering delays when an event reaches the SIEM, but the timestamp the device wrote into the event still reflects when it was generated, and the stem says those device timestamps are what the SIEM shows. Forwarding delay does not move a logon earlier in time.

Why not C? Deduplication removes identical copies of an event. It would not change timestamps or make a Kerberos request appear before the VPN session that produced it.

D is correct. Reliable correlation depends on time synchronization: every log source should sync to the same NTP hierarchy so events from different devices can be ordered. A device with a clock five minutes off makes a single attack look like two disconnected events, which is why logging configuration and time sync sit in objective 1.1.

Vulnerability Management

A vulnerability analyst at a county government runs weekly unauthenticated scans against 600 Windows servers. The reports list operating systems as probable guesses and miss most of the missing patches that the patch team knows are outstanding. Which change would give the analyst accurate patch and configuration data?

Why not A? Scanning the same way more often produces the same inaccurate results more often. Frequency does not fix the lack of visibility.

Why not B? An external scan shows what an internet attacker can reach, which is useful for a different question. It is still unauthenticated and will see less, not more, of each server's patch state.

Why not D? Passive scanning infers versions from observed traffic. It is gentler on fragile systems but even less precise about patch levels than an active unauthenticated scan.

C is correct. A credentialed (authenticated) scan logs in to the host and reads the installed patches, registry settings and software inventory directly instead of inferring them from banners and network responses. It produces far fewer false positives and negatives, which is why objective 2.1 treats the credentialed versus non-credentialed choice as a core scanning decision.

The full test has 50 questions like these. Start it now →

Start Your Free Practice Test

Enter your details, then choose a 25-question Quick Test or the full 50-question, 90-minute practice test.

First Name
Last Name
Phone

A Training Camp advisor may reach out about your results and study options. No spam, and you can opt out anytime.

Prefer to talk to someone?

What you get at the end

Your overall score, a score for each exam domain, and the domains to work on next.

Example report77%
Security Operations83%
Vulnerability Management64%
Incident Response and Management78%
Reporting and Communication71%
Below 80% is flagged as an area to work on.

What's on the CS0-004 exam

4 weighted domains. The practice test draws questions from each in the same proportion.

  • 34%

    Security Operations

    Log analysis, indicators of malicious activity, SIEM and EDR tooling, threat intelligence, and AI in the SOC.

  • 26%

    Vulnerability Management

    Scanning methods, reading scanner output, CVSS and KEV prioritization, remediation and compensating controls.

  • 24%

    Incident Response and Management

    Attack frameworks, the incident response lifecycle, containment, evidence handling, and root cause analysis.

  • 16%

    Reporting and Communication

    Vulnerability and incident reporting, stakeholder communication, metrics and KPIs, and after-action reviews.

Built on what our boot camp teaches

Every question maps to the same exam objectives we teach in the CySA+ boot camp, and every answer choice has its own explanation, so a wrong answer still teaches you something. Questions last reviewed September 29, 2026.

  • Real exam: a maximum of 85 questions in 165 minutes.
  • To pass: a scaled score of 750 on a scale of 100 to 900.
  • This test: 50 questions on a 90-minute timer, or a 25-question quick test.
Read the full CySA+ exam guide

This free CompTIA CySA+ practice test checks your readiness for the CS0-004 exam with 50 exam-style questions across all four domains, each with an explanation for every answer choice, on a 90-minute timer that mirrors the roughly two-minutes-per-question pace of the real exam. Built by Training Camp, an authorized CompTIA partner, and drawn from the same objectives we teach in our CySA+ Boot Camp. New to the exam? Learn more about the CySA+ certification.

What's on the CompTIA CySA+ (CS0-004) exam?

CS0-004 is the current version of the CompTIA Cybersecurity Analyst exam. It launched on June 23, 2026, and the CS0-003 English exam retires on December 22, 2026. The exam has four weighted domains: Security Operations (34%), Vulnerability Management (26%), Incident Response and Management (24%), and Reporting and Communication (16%). You get 165 minutes for a maximum of 85 questions, a mix of multiple-choice items and performance-based questions that drop you into a simulated console or log view, and you need a scaled score of 750 on a scale of 100 to 900 to pass.

The biggest change from CS0-003 is a new objective on AI in security operations inside the Security Operations domain: the risks of using AI tools (hallucinations, data exposure, model poisoning, malicious prompts), governance through usage policies, and practical use cases such as log analysis and event correlation. There are no formal prerequisites. CompTIA recommends CompTIA Network+, CompTIA Security+ or equivalent knowledge, plus about four years of hands-on work in a SOC analyst or vulnerability analyst role. The certification expires three years from the date you earn it and is renewed through CompTIA's continuing education program.

How to use this practice test

Take it once without notes to get an honest baseline, then read the explanation for every answer, including the ones you got right. The incorrect-choice explanations are where the distinctions the exam likes to test (atomic versus behavioral indicators, credentialed versus non-credentialed scans, CVSS base score versus active exploitation, containment versus eradication) get spelled out. Study your weakest domain and retake the test in a week. The 90-minute timer over 50 questions keeps you honest about pacing: the real exam gives you 165 minutes for up to 85 questions, so practice reading a log excerpt or scan result, deciding in about two minutes, and moving on.

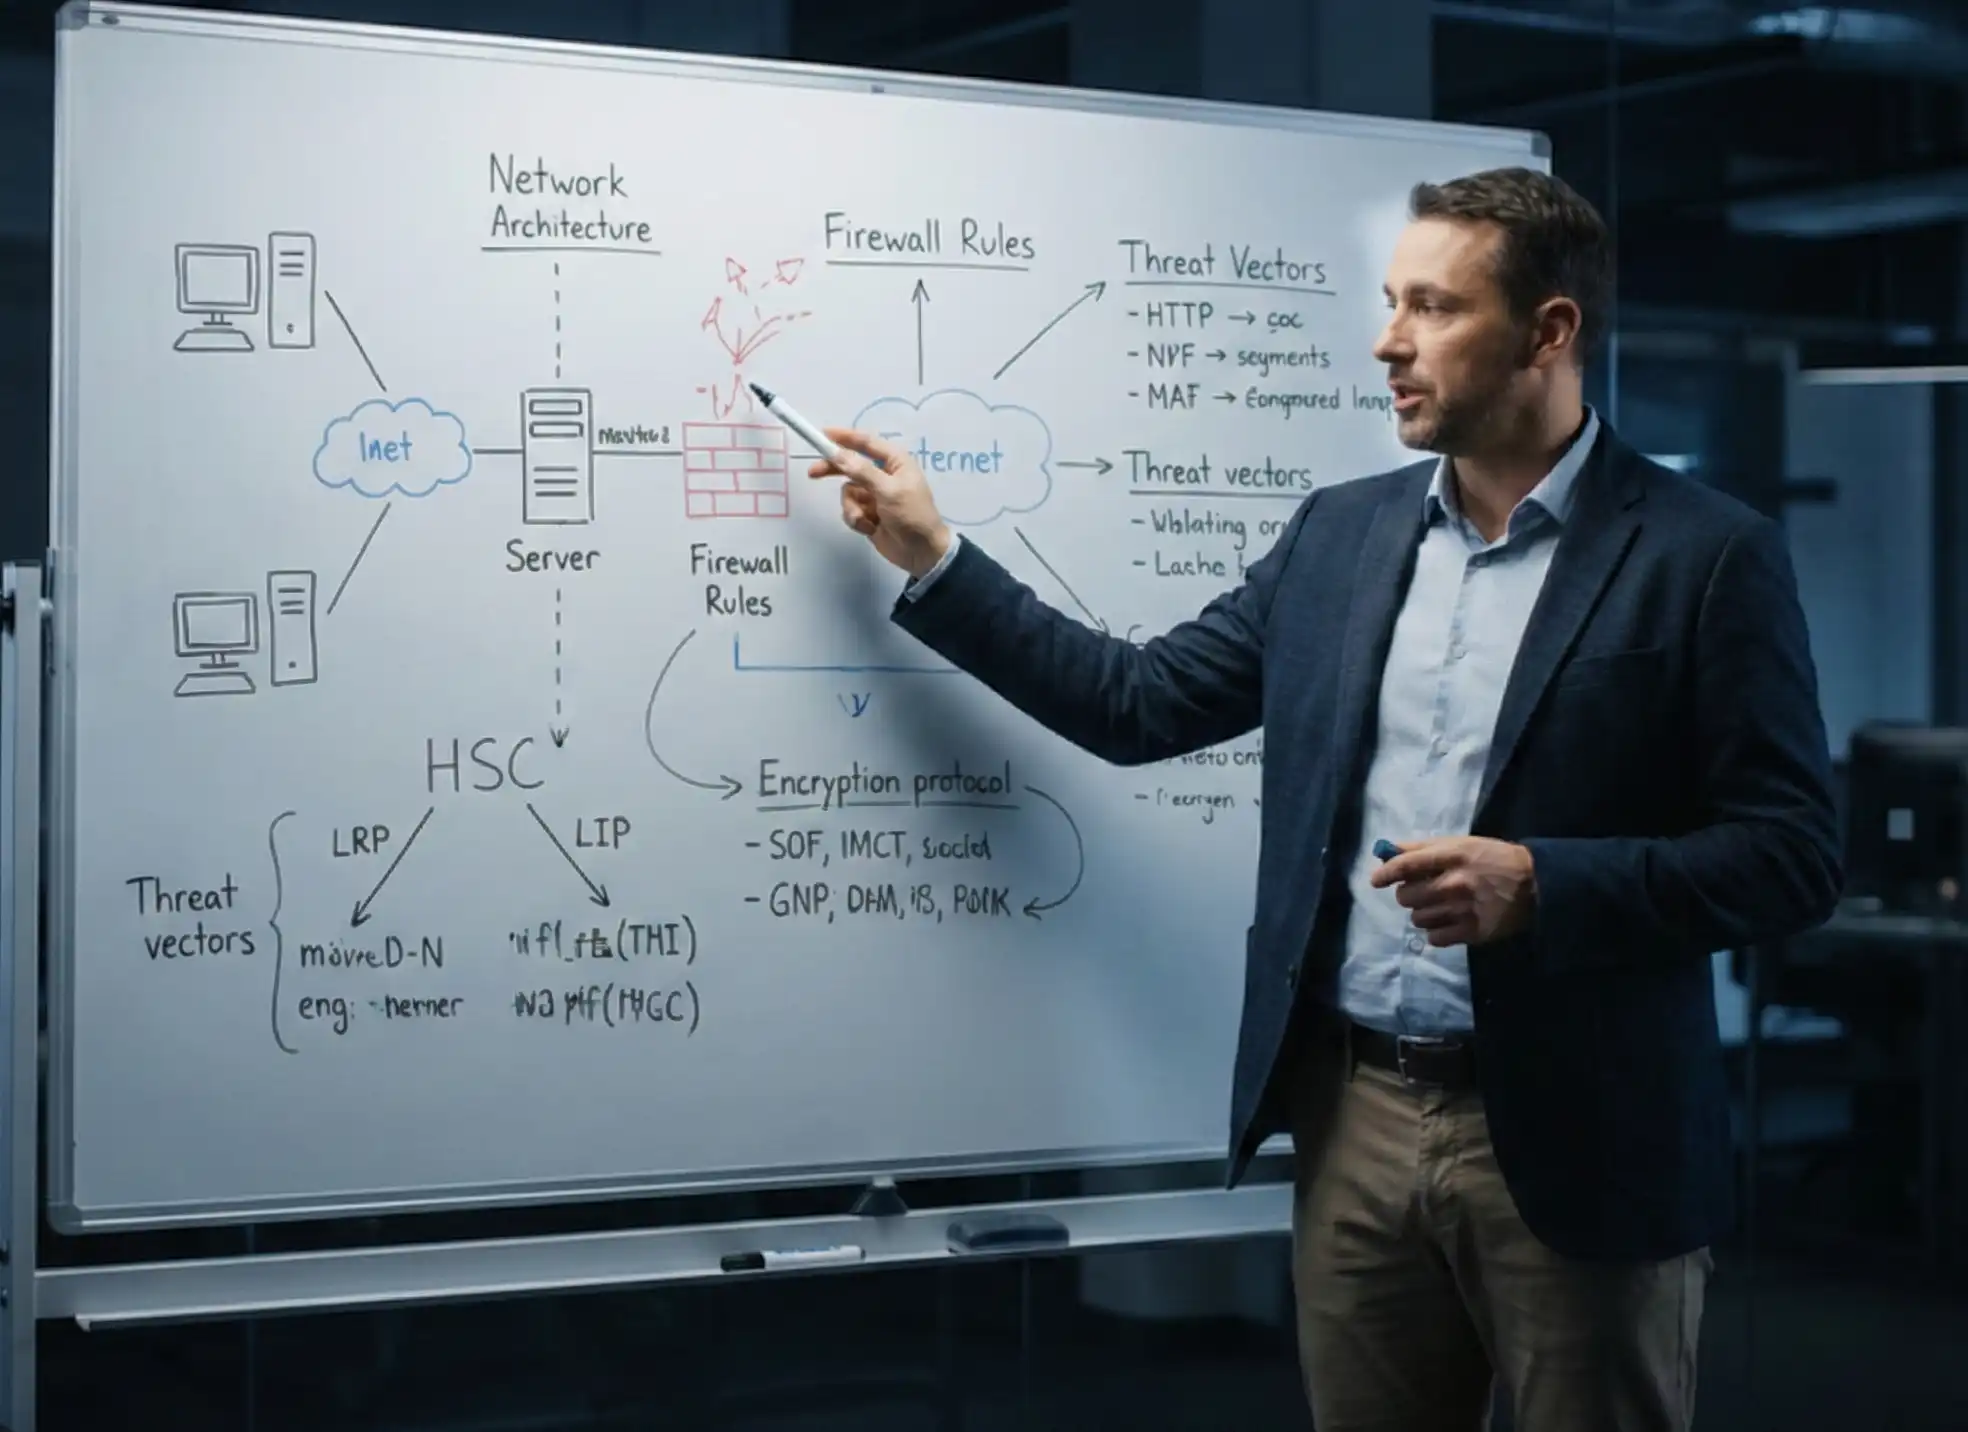
Training Camp instructor teaching network security at a whiteboard

How to get the most from it

Three steps, in this order.

Student working through practice questions at a laptop
Step 1

Take a baseline

Take the full test once without notes, so the score shows where you really stand.

Student reviewing material on a laptop
Step 2

Read every explanation

Including the ones you got right. The notes on the wrong choices explain the differences between similar concepts, like tokenization and encryption.

Students working on laptops in a Training Camp lab
Step 3

Fix one domain, then retake

Your results break down by domain. Study the weakest one for a week, then retake. Each Quick Test draws a fresh mix of questions.

CySA+ Practice Test

Frequently Asked Questions

Quick answers about the test, the CompTIA CySA+ (CS0-004) exam, and how to prepare.

Is this CySA+ practice test free?

Yes. Training Camp's CompTIA CySA+ practice test is free to take. You get 50 exam-style questions across all four CS0-004 domains, with a written explanation for every answer choice.

How does this practice test work?

It is 50 multiple-choice scenario questions drawn from all four CS0-004 domains, with an instant explanation after each answer and a 90-minute timer that mirrors the pace of the real exam. You can retake it as often as you want. Treat it as a readiness check rather than a substitute for full preparation.

How many questions are on the real CySA+ exam?

The CompTIA CySA+ CS0-004 exam has a maximum of 85 questions and a 165-minute time limit. It mixes multiple-choice items with performance-based questions that ask you to analyze logs, scan output or a simulated environment.

What score do I need to pass the CySA+ exam?

You need a scaled score of 750 on a scale of 100 to 900 to pass the CompTIA CySA+ CS0-004 exam.

What domains does the CySA+ CS0-004 exam cover?

CS0-004 covers four domains: Security Operations (34%), Vulnerability Management (26%), Incident Response and Management (24%), and Reporting and Communication (16%). Security Operations is the largest and now includes an objective on AI in security operations.

What changed between CySA+ CS0-003 and CS0-004?

CS0-004 launched on June 23, 2026 and keeps the same four domain names, but the weights moved from 33/30/20/17 in CS0-003 to 34/26/24/16. It adds AI in security operations as a new objective (1.6), covering AI risks, governance and use cases in the SOC, and CompTIA also cites expanded EPSS-based prioritization, Zero Trust and SASE architecture, and SBOM and software supply chain coverage. The CS0-003 English exam retires on December 22, 2026.

Do I need experience to take the CySA+ exam?

There are no formal prerequisites. CompTIA recommends CompTIA Network+, CompTIA Security+ or equivalent knowledge, plus about four years of hands-on work in a SOC analyst or vulnerability analyst role. The exam assumes you have read real logs and scan results, so lab time matters as much as reading.

How should you prepare for the CySA+ exam?

Start with the CS0-004 exam objectives and get hands-on with a SIEM, a packet analyzer and a vulnerability scanner, then use practice questions like these to find your weak domains. If you want a structured path with an instructor and your exam voucher included, our CySA+ Boot Camp covers all four domains.

Instructor-led Training Camp class

Ready to pass it for real?

The CySA+ boot camp covers every exam domain with a live instructor, online or in person.

  • Exam voucher included
  • Free retake
  • 180 days of unlimited 1-on-1 coaching after class