Hello, you are using an old browser that's unsafe and no longer supported. Please consider updating your browser to a newer version, or downloading a modern browser.

Splunk Certification Exam Prep Training

Splunk Core Certified Power User

Stop running other people’s searches and start building them. Four days of official Splunk courseware, and the first step on every Splunk certification track.

Verified for 2026 SPLK-1002 Exam
Student
Student
Student
Join 250,000+ certified alumni.
CISSP Professional

Official Content

Splunk Education courseware

Valid 3 Years

Splunk, a Cisco company

Official Splunk Education course, delivered live online through our Splunk Authorized Learning Partner

Splunk Core Certified Power User. Certified in Four Days.

4 days for SOC analysts, IT operations staff and anyone who searches Splunk daily and wants to build the knowledge objects behind it.

Program Abstract

REF: SPLK-1002 10
Curriculum aligned to the latest Exam Outline.
Format Live Online, Instructor-Led
Duration 4

The Splunk Core Certified Power User Boot Camp

Splunk Core Certified Power User is the required first step for every Splunk certification, including both admin tracks.

Nine Official Topics, 60+ Commands.

The official Splunk Education Power User Fast Start course, nine topics in Splunk’s published order from Working with Time through Data Models, covering more than 60 commands, functions and knowledge objects.

Official Splunk Courseware.

Official Splunk Education courseware and labs, delivered live online by Splunk-authorized instructors through our Splunk Authorized Learning Partner.

Labs on a Real Splunk Instance.

Hands-on labs in a provided Splunk environment with nothing to install, so you write the searches, extract the fields and build the data models yourself.

·
Training materials including official courseware and study guides
Practitioner Led
Instructors are working security professionals, not just trainers.

"I don't teach from a textbook. I teach what happens in the SOC when the alert fires."

Jeff Porch

VP Ed. Services • CISSP, CISM CISSP: Certified Information Systems Security Professional. CISM: Certified Information Security Manager.

Choose Your Delivery Mode.

Same Curriculum
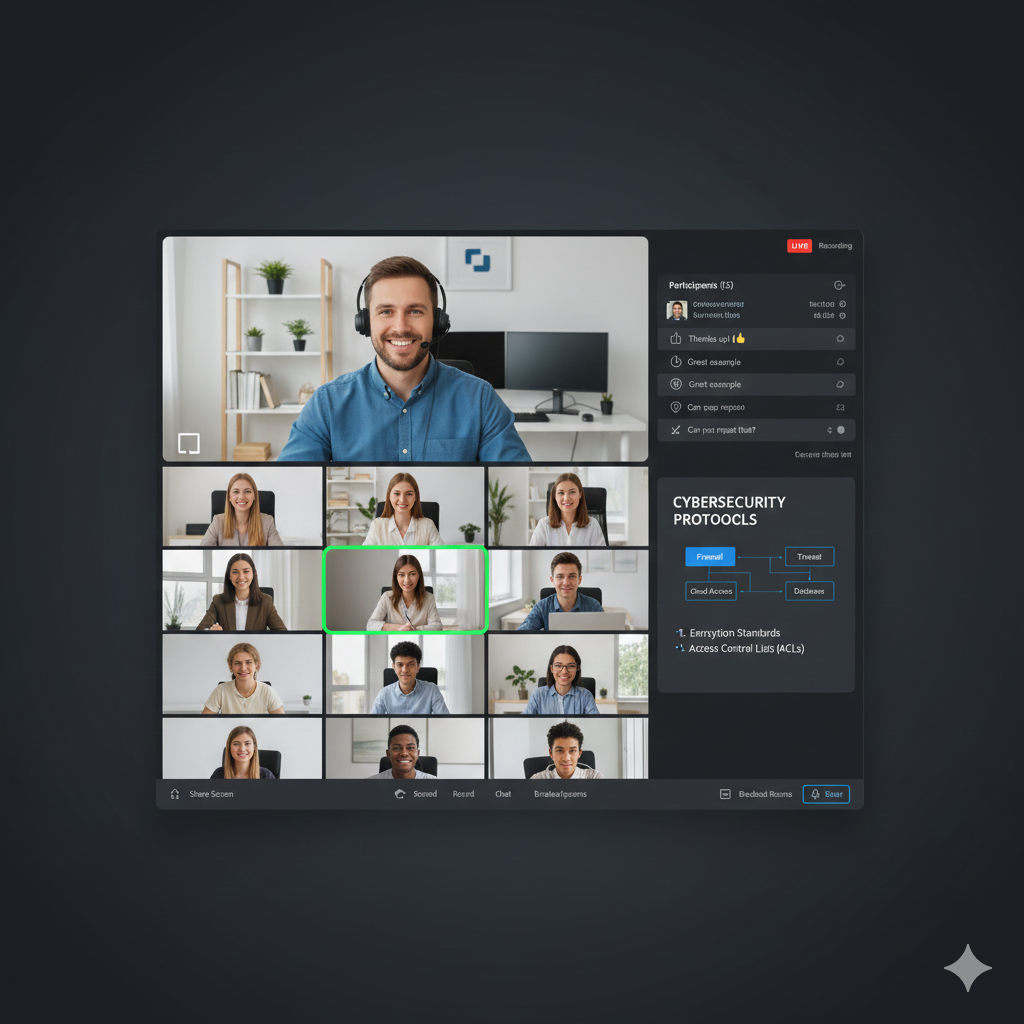
Student attending live online training
A

Live Online

Delivered live online in a virtual classroom, with the official curriculum, hands-on labs and a Splunk-authorized instructor.

  • Live online, no travel required
  • Eastern Time schedule
Offer

Save on this course with a current special offer

Team pricing, military discounts and a limited-time offer of the week. See what applies before you book.

See special offers
Get Started Today

Explore Your Training Options

Tell us about your training needs and we'll create a personalized plan.

Official Splunk Education Content

Official Splunk Education Courseware

This is Splunk’s own Power User Fast Start course, nine official topics covering more than 60 commands, functions and knowledge objects, not a third-party syllabus.

Splunk-Authorized Instructors

Taught by Splunk-Authorized Instructors

Delivered live online through our Splunk Authorized Learning Partner by instructors certified by Splunk Education to teach this course.

Hands-On Labs

Hands-On Labs, Nothing to Install

A provided Splunk environment with sample data indexed, so you run eval, transaction and pivot on real events rather than slides.

Blueprint Alignment

Maps to All Ten SPLK-1002 Exam Areas

The nine course topics cover the full published SPLK-1002 blueprint, from transforming commands at 5% to correlating events at 15%.

Required First Step

The Required First Step in the Splunk Track

Power User is the prerequisite for Splunk Enterprise Certified Admin and Splunk Cloud Certified Admin, so this one credential opens both admin paths.

Enrollment Made Simple

We Handle Enrollment, GSA and Vouchers

Training Camp manages your enrollment and invoicing, accepts training vouchers and GSA Schedule purchases, and schedules private team cohorts.

Splunk Core Certified Power User Boot Camp (SPLK-1002)

Accepting Inquiries
+1

    Eligible for Special Pricing?

    We respect your privacy. No spam.

    COURSE STRUCTURE

    Splunk Core Certified Power User Boot Camp (SPLK-1002) Course Outline
    Outline

    A structured path designed for working professionals.
    Each day builds on the last—momentum is everything.

    Request Info

    MODULE_ID: PREP

    Live Training QS: ~5
    BEFORE CLASS
    Critical Path

    Before Class

    Nothing needs installing on your machine.
    L.prep.1
    Class runs 10:00 AM to 6:00 PM Eastern each day.
    L.prep.2
    The SPLK-1002 exam is not included; you book it with Pearson VUE after class.
    L.prep.3

    MODULE_ID: SPLK-1002-01

    Live Training QS: ~5
    DAY 1
    Critical Path

    Working with Time and Statistical Processing

    Time Range Picker, Relative Time Modifiers and Snap-To Units
    L.01.1
    Using _time, earliest, latest and the bin Command
    L.01.2
    Formatting Time With strftime, strptime and relative_time
    L.01.3
    Time Zones, Indexed Time and the date_* Fields
    L.01.4
    timechart Command, span and the limit Argument
    L.01.5
    Choosing Visualizations for Time-Based Results
    L.01.6
    Lab: Build a timechart of Failed Logins by Source IP
    L.01.7
    Lab: Compare This Week to Last Week With Time Modifiers
    L.01.8
    Transforming Commands: stats, chart and timechart Compared
    L.01.9
    chart Command With over and by Clauses
    L.01.10
    Statistical Functions: count, dc, avg, sum, list and values
    L.01.11
    Splitting Results With by Fields and useother, usenull
    L.01.12
    eventstats and streamstats for Running Calculations
    L.01.13
    Formatting Output With fieldformat, rename and tostring
    L.01.14
    Lab: Chart Sales by Product Category and Region
    L.01.15
    Lab: Add Running Totals With streamstats
    L.01.16

    MODULE_ID: SPLK-1002-02

    Live Training QS: ~6
    DAY 2
    Critical Path

    Comparing Values and Result Modification

    eval Command Functions for Math, Strings and Conversion
    L.02.1
    Conditional Logic With if, case, match and coalesce
    L.02.2
    where Command Versus search for Field Comparisons
    L.02.3
    Comparison Operators, Wildcards and the like Function
    L.02.4
    fillnull Command and Handling Missing Field Values
    L.02.5
    Rounding, Type Conversion and tonumber, tostring
    L.02.6
    Lab: Use eval and where to Flag Slow HTTP Requests
    L.02.7
    Lab: Clean Null Fields With fillnull Before Reporting
    L.02.8
    sort, head, tail and dedup for Controlling Result Sets
    L.02.9
    fields and table Commands for Shaping Output
    L.02.10
    Multivalue Fields With makemv, mvexpand and mvcount
    L.02.11
    Creating Fields With rex and erex at Search Time
    L.02.12
    Subsearches, Their Limits and the format Command
    L.02.13
    Lookups With lookup, inputlookup and outputlookup
    L.02.14
    Lab: Enrich Web Logs With a Status Code Lookup
    L.02.15
    Lab: Split Multivalue Recipient Fields With mvexpand
    L.02.16

    MODULE_ID: SPLK-1002-03

    Live Training QS: ~6
    DAY 3
    Critical Path

    Correlation Analysis and Knowledge Objects

    transaction Command Syntax and Grouping by Common Fields
    L.03.1
    maxspan, maxpause and maxevents Constraints
    L.03.2
    startswith and endswith for Defining Transaction Boundaries
    L.03.3
    Transaction Fields: duration, eventcount and closed_txn
    L.03.4
    transaction Versus stats: Performance and Use Cases
    L.03.5
    Finding Incomplete Transactions With keepevicted and keeporphans
    L.03.6
    Lab: Trace a Customer Purchase Across Web Sessions
    L.03.7
    Lab: Rewrite a transaction Search Using stats
    L.03.8
    Knowledge Object Types, Naming Conventions and Permissions
    L.03.9
    Field Aliases for Normalizing Field Names Across Sourcetypes
    L.03.10
    Calculated Fields With eval Expressions in Settings
    L.03.11
    Creating Tags on Field-Value Pairs and Searching With tag=
    L.03.12
    Event Types: Definition, Priority, Color and eventtype Field
    L.03.13
    Search Macros With Arguments and Validation Expressions
    L.03.14
    Workflow Actions: GET, POST and Search Types With $field$ Tokens
    L.03.15
    Lab: Build a Macro, Event Type and GET Workflow Action
    L.03.16

    MODULE_ID: SPLK-1002-04

    Live Training QS: ~7
    DAY 4
    Critical Path

    Field Extractions and Data Models

    Field Extractor Workflow: Regular Expression Method
    L.04.1
    Field Extractor Workflow: Delimiter Method for Structured Data
    L.04.2
    Regex Fundamentals: Character Classes, Quantifiers and Capture Groups
    L.04.3
    Validating and Editing Extractions in Settings and props.conf
    L.04.4
    Search-Time Versus Index-Time Extraction Trade-Offs
    L.04.5
    Managing Extraction Permissions and Sharing Across Apps
    L.04.6
    Lab: Extract username and action Fields With Regex
    L.04.7
    Lab: Extract Pipe-Delimited Fields From a Custom Log
    L.04.8
    Data Model Structure: Root Events, Searches and Transactions
    L.04.9
    Adding Attributes: Auto-Extracted, eval, Lookup and Regex
    L.04.10
    Building Reports and Dashboards With the Pivot Editor
    L.04.11
    Common Information Model Add-On and CIM Field Normalization
    L.04.12
    Lab: Build a Web Data Model and Pivot Report
    L.04.13
    Lab: Map a Custom Sourcetype to the CIM Authentication Model
    L.04.14
    Course Review and Key Takeaways
    L.04.15
    Next Step: Schedule SPLK-1002 With Pearson VUE
    L.04.16

    MODULE_ID: POST

    Live Training QS: ~7
    AFTER CLASS
    Critical Path

    After Class

    When the course ends you keep your official Splunk Education courseware and lab notes for revision.
    L.post.1
    COURSE PROGRESS Day 0 of 4
    Splunk Certification Track

    Master the SPLK-1002 Exam 4 Days to Certified

    Nine official Splunk Education topics that map to all 10 SPLK-1002 exam areas, with hands-on labs throughout.

    Splunk Power User boot camp Splunk Power User Fast Start Splunk Core Certified Power User training SPLK-1002 training Splunk Power User boot camp Splunk Power User Fast Start Splunk Core Certified Power User training SPLK-1002 training
    official Splunk Education course Splunk knowledge objects training SPLK-1002 official Splunk Education course Splunk knowledge objects training SPLK-1002
    Frequently Asked Questions

    SPLK-1002 Boot Camp Questions, Answered
    SPLK-1002

    Real questions from real professionals who passed.
    Here's how we answer them.

    Splunk Core Certified Power User, earned by passing exam SPLK-1002. It is the entry-level certification from Splunk, a Cisco company, and confirms you can use the search language, build knowledge objects and work with data models.

    No prerequisite exam is required. Splunk does assume you know how Splunk works and can perform basic searching and visualizations, roughly the level of its Intro to Splunk and Using Fields courses. If you have never used Splunk, work through Splunk’s free Intro to Splunk and Using Fields eLearning first.

    4 days, live online, 10:00 AM to 6:00 PM Eastern, for 32 hours in total. It is the official Splunk Education Power User Fast Start course, delivered through our Splunk Authorized Learning Partner.

    No. The SPLK-1002 exam is purchased separately by the student after class, directly from Pearson VUE, at $130 per attempt. The course price covers instruction, official courseware and labs only.

    65 multiple-choice questions in 60 minutes, which includes 3 minutes to review the exam agreement. The exam is delivered by Pearson VUE, online or at a test center.

    Ten areas, weighted as published by Splunk: Transforming Commands for Visualizations (5%), Filtering and Formatting Results (10%), Correlating Events (15%), Creating and Managing Fields (10%), Field Aliases and Calculated Fields (10%), Tags and Event Types (10%), Macros (10%), Workflow Actions (10%), Data Models (10%) and Common Information Model Add-On (10%).

    SOC analysts, IT operations staff and anyone who searches Splunk every day and wants to build the knowledge objects, dashboards and data models that other people use. It is also the required first step for anyone heading toward a Splunk admin certification.

    Yes. Splunk requires the Power User certification before you can earn Splunk Enterprise Certified Admin or Splunk Cloud Certified Admin. You then choose one admin track, Enterprise for self-managed Splunk Enterprise or Cloud for Splunk Cloud Platform, and do not need both.

    Splunk certifications are valid for three years. To stay current you retake the exam or earn a higher certification in the track before it expires.

    One of the two admin certifications: our Splunk Enterprise Certified Admin Boot Camp for self-managed Splunk Enterprise, or our Splunk Cloud Certified Admin Boot Camp for Splunk Cloud Platform. Advanced Power User Fast Start, Enterprise Administration Fast Start and Using Splunk Enterprise Security are also available through us on request.

    You can schedule another attempt with Pearson VUE, at $130 per attempt, subject to Splunk’s retake policy. You keep your official courseware and lab notes to review the areas that gave you trouble.

    Yes. We arrange private live online cohorts for your team to your own schedule, with Training Camp handling enrollment and invoicing. Contact us with your head count and preferred dates.

    Yes. Training Camp handles GSA Schedule purchasing and accepts training vouchers for this course. Our government sales team can walk you through the paperwork. Many of our courses are also approved for VA education benefits; check eligibility before enrolling.

    It is the gateway to every other Splunk certification, so if you plan to administer Splunk at all it is not optional. It also covers the knowledge objects and data models that separate someone who runs searches from someone who builds what the rest of the team searches with.

    SOC analysts, security engineers, IT operations and site reliability staff, and anyone building Splunk dashboards, alerts and reports for others. It is also the standard stepping stone for Splunk administrators.

    Get the Free
    SPLK-1002 Exam Guide

    • Expert strategies to spot trick questions
    • Question patterns examiners actually use
    • Proven pacing + pressure management tactics
    Articles and Certification Resources

    SPLK-1002 Articles and Exam News
    Articles and Exam News

    Exam changes, study guidance and career context for SPLK-1002, from our instructors.

    Student Success Stories

    What Our Students Say

    Join thousands of certified professionals who trained with Training Camp

    ★★★★★

    Instructor Jarrett Heintz went above and beyond to give us everything we could possibly need to take the exam. There were tons of resources he provided and on to...

    SC
    Sav**** Coo*** L** County Commission – Systems Administrator
    ★★★★★

    A must stop-by resort before any certification test. Teachers teach you something for life, rather than only for certification.

    Continue Your Journey

    Splunk Core Certified Power User Related Courses

    Advance your career with these recommended certifications

    Featured on