Hello, you are using an old browser that's unsafe and no longer supported. Please consider updating your browser to a newer version, or downloading a modern browser.

Free Practice Test

Free CEH Practice Test
for v13 · 312-50

Check your readiness for the EC-Council Certified Ethical Hacker (CEH v13) 312-50 exam with 50 scenario questions built from the official 20 modules, each with an instant explanation. Free to take, timed with a 90-minute limit set to the pace of the real exam, and yours to retake as often as you want.

50Questions, or a 25-question quick test
90 minTimer, paced like the real exam
7v13 · 312-50 domains covered
A–DEvery answer choice explained, right and wrong

Try a question before you start

Pick an answer to see the reasoning. These are samples from the 50-question bank; the full test starts below.

Ethical Hacking Fundamentals

A penetration tester has a signed engagement and has finished gathering open-source intelligence and scanning the target range. They now begin exploiting a validated vulnerability to obtain a foothold on a host. Which phase of the ethical hacking lifecycle does this activity BEST represent?

Why not B? Scanning maps live hosts, ports and services. It comes before exploitation, not during it.

Why not C? Reconnaissance is the information-gathering phase that precedes exploitation. The tester has already completed it.

Why not D? Clearing tracks (covering tracks) is the final phase of removing evidence of activity. It happens after access is gained, not while exploiting.

A is correct. Gaining access is the phase where the tester exploits a validated weakness to obtain a foothold or elevate privileges on a target. It follows reconnaissance and scanning.

Reconnaissance, Scanning and Enumeration

During the footprinting phase, an analyst wants to learn about a target organization's employees, technologies and subdomains without sending any traffic to the organization's own systems. Which approach BEST fits this requirement?

Why not B? A TCP connect scan sends packets straight at the target. That is active reconnaissance, and it leaves connection logs behind.

Why not C? Banner grabbing opens a connection to each service to read its version string, so the target sees the traffic.

Why not D? A zone transfer request goes directly to the target's name server. Active, not passive.

A is correct. Passive reconnaissance gathers intelligence from third-party and public sources such as search engines, social media and registries without interacting with the target's systems, so it leaves no trace on them.

The full test has 50 questions like these. Start it now →

Start Your Free Practice Test

Enter your details, then choose a 25-question Quick Test or the full 50-question, 90-minute practice test.

First Name
Last Name
Phone

A Training Camp advisor may reach out about your results and study options. No spam, and you can opt out anytime.

Prefer to talk to someone?

What you get at the end

Your overall score, a score for each exam domain, and the domains to work on next.

Example report77%
Ethical Hacking Fundamentals83%
Reconnaissance, Scanning and Enumeration64%
System Hacking and Malware78%
Network Attacks and Evasion71%
Web Application Attacks90%
Wireless, Mobile, IoT and OT83%
Cloud and Cryptography64%
Below 80% is flagged as an area to work on.

What's on the v13 · 312-50 exam

7 weighted domains. The practice test draws questions from each in the same proportion.

  • Module 1

    Ethical Hacking Fundamentals

    Hacking phases, attacker types, scope and authorization.

  • Modules 2-5

    Reconnaissance, Scanning and Enumeration

    Footprinting, OSINT, port scanning and service enumeration.

  • Modules 6-7

    System Hacking and Malware

    Gaining access, privilege escalation, persistence and malware types.

  • Modules 8-12

    Network Attacks and Evasion

    Sniffing, social engineering, DoS, session hijacking and IDS evasion.

  • Modules 13-15

    Web Application Attacks

    Web server flaws, web application attacks and SQL injection.

  • Modules 16-18

    Wireless, Mobile, IoT and OT

    Wireless attacks, mobile platform risks, and IoT and OT security.

  • Modules 19-20

    Cloud and Cryptography

    Cloud security models and applied cryptography concepts.

Built on what our boot camp teaches

Every question maps to the same exam objectives we teach in the CEH boot camp, and every answer choice has its own explanation, so a wrong answer still teaches you something. Questions last reviewed September 29, 2026.

  • Real exam: 125 multiple-choice questions in 4 hours.
  • To pass: a cut score that varies between 60% and 85% depending on the difficulty of the exam form.
  • This test: 50 questions on a 90-minute timer, or a 25-question quick test.
Read the full CEH exam guide

This free EC-Council Certified Ethical Hacker (CEH v13) practice test checks your readiness for the 312-50 knowledge exam with 50 scenario questions built from the official 20 modules, each with an explanation for every answer choice. It is built by Training Camp, an EC-Council Accredited Training Center. New to the exam? Learn what the CEH certification is, or see the accelerated CEH Boot Camp.

What's on the EC-Council Certified Ethical Hacker (CEH v13) exam?

The CEH v13 knowledge exam (312-50) has 125 multiple-choice questions and a 4-hour time limit, delivered through Pearson VUE or EC-Council's exam portal. The certification is organized into 20 modules and, in v13, adds AI-driven techniques woven through the attack lifecycle.

EC-Council's current CEH Exam Blueprint (v5.0) organizes the 125 questions into nine weighted domains: Information Security and Ethical Hacking Overview (6%), Reconnaissance Techniques (17%), System Hacking Phases and Attack Techniques (15%), Network and Perimeter Hacking (24%), Web Application Hacking (14%), Wireless Network Hacking (5%), Mobile Platform, IoT, and OT Hacking (10%), Cloud Computing (5%) and Cryptography (5%). The seven topic areas in this practice test are our own groupings of the 20 modules that sit under those domains, from ethical hacking fundamentals and reconnaissance through system hacking, network attacks, web application attacks, wireless and IoT, and cloud and cryptography.

How to use this practice test

Every question is an original, scenario-style item that frames you as a penetration tester working under a signed engagement, a security analyst, or an exam candidate identifying the right tool, phase, countermeasure or indicator. The test runs 50 questions on a 90-minute timer, and after each answer you get an explanation for the correct choice and for every distractor, so a wrong answer becomes a learning moment.

Take it timed to build exam stamina, review the per-topic breakdown at the end, and retake it as often as you want. Treat it as a readiness check that points you toward the modules to study, not as a substitute for full preparation.

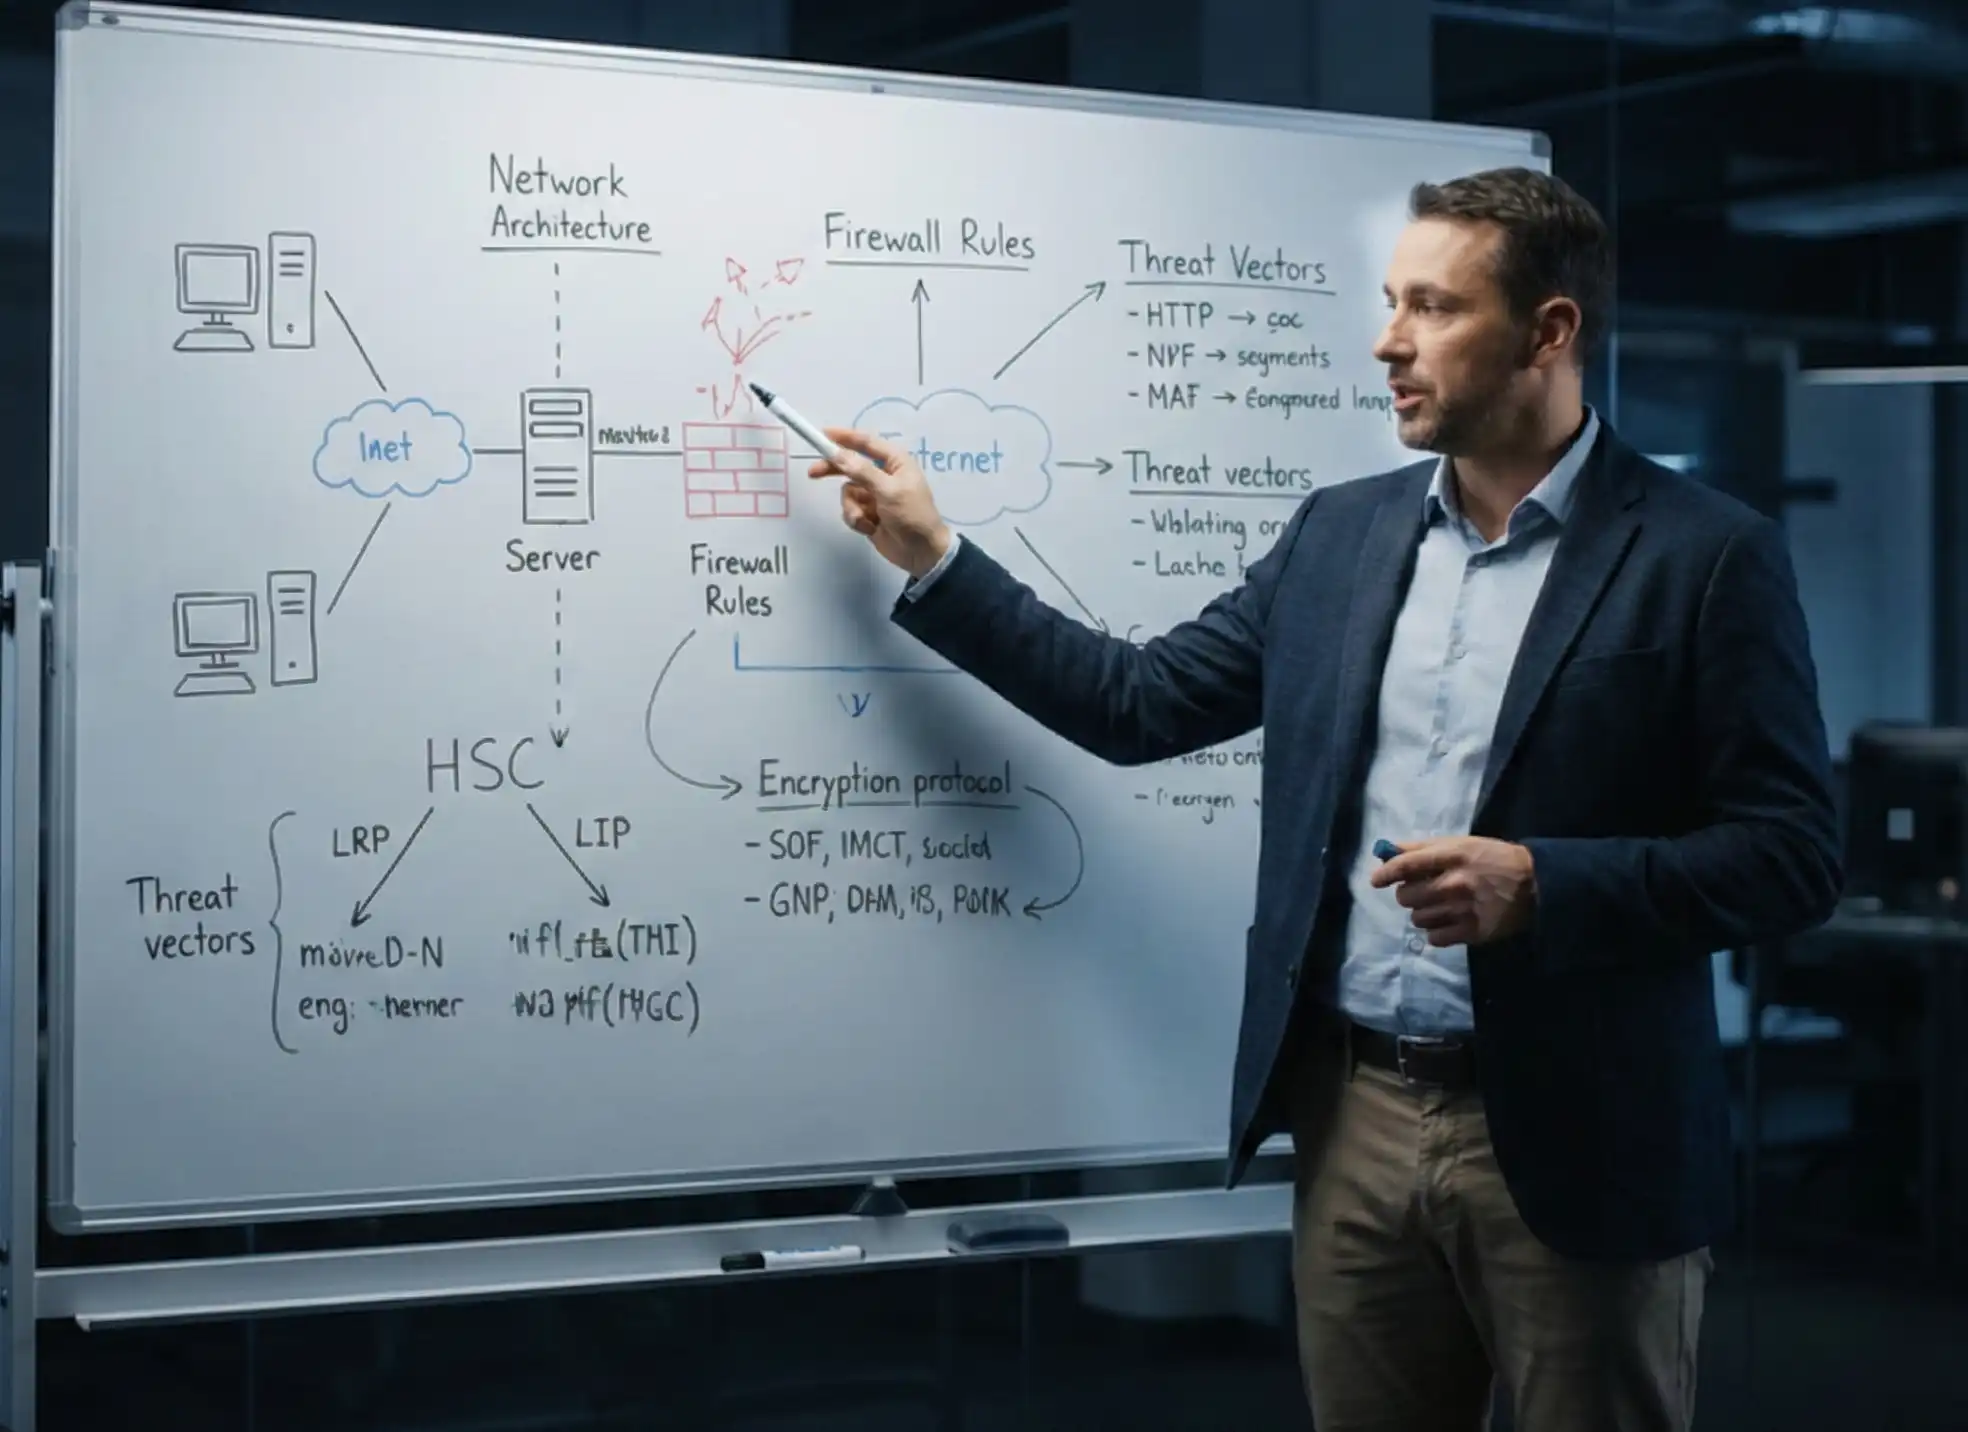
Training Camp instructor teaching network security at a whiteboard

How to get the most from it

Three steps, in this order.

Student working through practice questions at a laptop
Step 1

Take a baseline

Take the full test once without notes, so the score shows where you really stand.

Student reviewing material on a laptop
Step 2

Read every explanation

Including the ones you got right. The notes on the wrong choices explain the differences between similar concepts, like tokenization and encryption.

Students working on laptops in a Training Camp lab
Step 3

Fix one domain, then retake

Your results break down by domain. Study the weakest one for a week, then retake. Each Quick Test draws a fresh mix of questions.

CEH Practice Test

Frequently Asked Questions

Quick answers about the test, the EC-Council Certified Ethical Hacker (CEH v13) exam, and how to prepare.

Is this CEH practice test free?

Yes. Training Camp's CEH practice test is free to take. You get 50 original scenario questions built from the EC-Council Certified Ethical Hacker (CEH v13) modules, with a written explanation for every answer choice.

How does this practice test work?

It is 50 multiple-choice questions drawn from the 20 CEH v13 modules, with an instant explanation after each answer and a 90-minute timer that is set to the pace of the real exam. You can retake it as often as you want. It is a readiness check, not a substitute for full preparation.

How many questions are on the real CEH exam?

The CEH v13 knowledge exam (312-50) has 125 multiple-choice questions and a 4-hour time limit. It is delivered through Pearson VUE or EC-Council's exam portal.

What score do I need to pass the CEH exam?

EC-Council does not publish a fixed passing score for the CEH exam. The cut score varies between 60% and 85% depending on the difficulty of the exam form you receive.

What topics does the CEH v13 exam cover?

CEH v13 covers 20 modules, and v13 adds AI-driven techniques across the attack lifecycle. EC-Council's CEH Exam Blueprint (v5.0) groups the exam into nine weighted domains, with Network and Perimeter Hacking (24%) and Reconnaissance Techniques (17%) carrying the most questions. The topic groupings in this test, such as reconnaissance, system hacking, network attacks, web application attacks, wireless and IoT, and cloud and cryptography, are ours, built from the 20 modules.

Is the CEH exam hard, and are there prerequisites?

CEH is an intermediate certification. EC-Council expects familiarity with networking, operating systems and security fundamentals, and either official training or at least two years of documented information security work experience. Practicing with scenario questions is one of the most effective ways to prepare.

How should I prepare for the CEH exam?

Combine hands-on lab practice with structured study across all 20 modules. Beyond practice questions, consider the accelerated CEH Boot Camp, which includes an exam voucher and a free retake option.

Using your GI Bill®?

If you are a veteran or service member, your benefits can pay for CEH prep.

  • Post-9/11 GI Bill®: our live online CEH Certification Exam Preparatory Course is approved for Chapter 33 benefits, and the VA can reimburse the exam fee as well. See the GI Bill® prep course →
U.S. Army service member working on a laptop
Instructor-led Training Camp class

Ready to pass it for real?

The CEH boot camp covers every exam domain with a live instructor, online or in person.

  • Exam voucher included
  • Free retake
  • 180 days of unlimited 1-on-1 coaching after class