
Hello, you are using an old browser that's unsafe and no longer supported. Please consider updating your browser to a newer version, or downloading a modern browser.

Training Camp's 5-day EC-Council CEH v13 boot camp covers ethical hacking techniques, penetration testing tools, and attack methodologies. Exam voucher and free retake included.

EC-Council Partner of the Year

EC-Council CEH Boot Camp

Official EC-Council CEH v13 Boot Camp. Master ethical hacking and penetration testing across all 20 modules, including the new AI-driven attack techniques. Mobile app, exam voucher, free retake, and hands-on labs included.

Verified for 2026 CEH-v13 Exam
Student
Student
Student
Join 250,000+ certified alumni.
CISSP Professional

Free Retake

Exam Protection Included

Official EC-Council

Authorized Training

Proven by 50,000+. Backed by our Free Retake Guarantee

Start Monday. Test Friday. No Waiting. No Risk.

5 days designed for security professionals ready to move into offensive security roles. Walk out exam-ready with our free retake guarantee.

Program Abstract

REF: CEH-v13 20
Curriculum aligned to the latest Exam Outline.
Format Live, Instructor-Led
Duration 5

The CEH is Hard. We Know How to Pass It.

Think like an attacker, defend like a professional. Our CEH v13 boot camp is an intensive 5-day Certified Ethical Hacker training covering all 20 EC-Council modules — reconnaissance, scanning, system hacking, web and wireless attacks, cloud, cryptography, and the AI-driven techniques new to v13. Pass the CEH 312-50 exam by Friday.

Official EC-Council CEH Training.

Third-party materials can’t keep up with exam changes. We use EC-Council’s authorized courseware, so you’re studying exactly what’s on the test — not outdated guesswork.

System Integrity Check
Content Source EC-Council Official
Curriculum Ver. 2026v2
Instructor Auth. Verified
Exam Alignment 100% MATCH

CEH Exam Fee Included.

$1,199 exam voucher included with your enrollment. No surprise costs, no last-minute purchases, just focus on passing.

Mobile Learning

Start Right Away

Unlock iOS/Android app immediately upon enrollment.

Authorized Material

Course from the Source

Official courseware, matched to the current exam version.

All-Inclusive

Exam Fee Included

We cover your $1,199 exam fee. No hidden costs.

Sim Engine

Exam Deja Vu

Practice with exam-style questions. No surprises.

Retake Policy

Exam Protection Included

Unlimited class returns if you need a second shot.

Flexible Schedule

Training Fits Your Life

Day, evening, online or in-person—your choice.

Test Center

Test While It's Fresh

Take your exam on-site within 7 days of class.

Expert Support

Never On Your Own

180 days of unlimited 1-on-1 coaching after class.

Test Friday. No Waiting.

Our private Pearson VUE testing center means you take your exam immediately after class. No scheduling delays, no waiting weeks to test while knowledge fades.

Friday 5PM
Bootcamp Concludes - You leave with a personalized attack plan.
Class Ends
Unlimited 1-on-1
AI Gap Analysis - We identify your weak domains using our simulation engine.
Gap Analysis
Exam Day
Exam Protection Active - If you don't pass, your next seat is free.
Certified
·
Training materials including official courseware and study guides
Practitioner Led
Our instructors work in the fields they teach, not just in the classroom.

"I teach what works on real engagements, and how to write it up so it gets fixed."

Eric Beasley

Lead Instructor • CISSP, CEH All of our trainers carry a wide range of certifications, including the certification for every program they teach or manage.

Choose Your Delivery Mode.

Same Curriculum
In-person classroom training session
A

In-Person

Immersive classroom instruction with direct instructor access, hands-on labs and peer collaboration.

  • Face-to-face instruction
  • On-site exam option
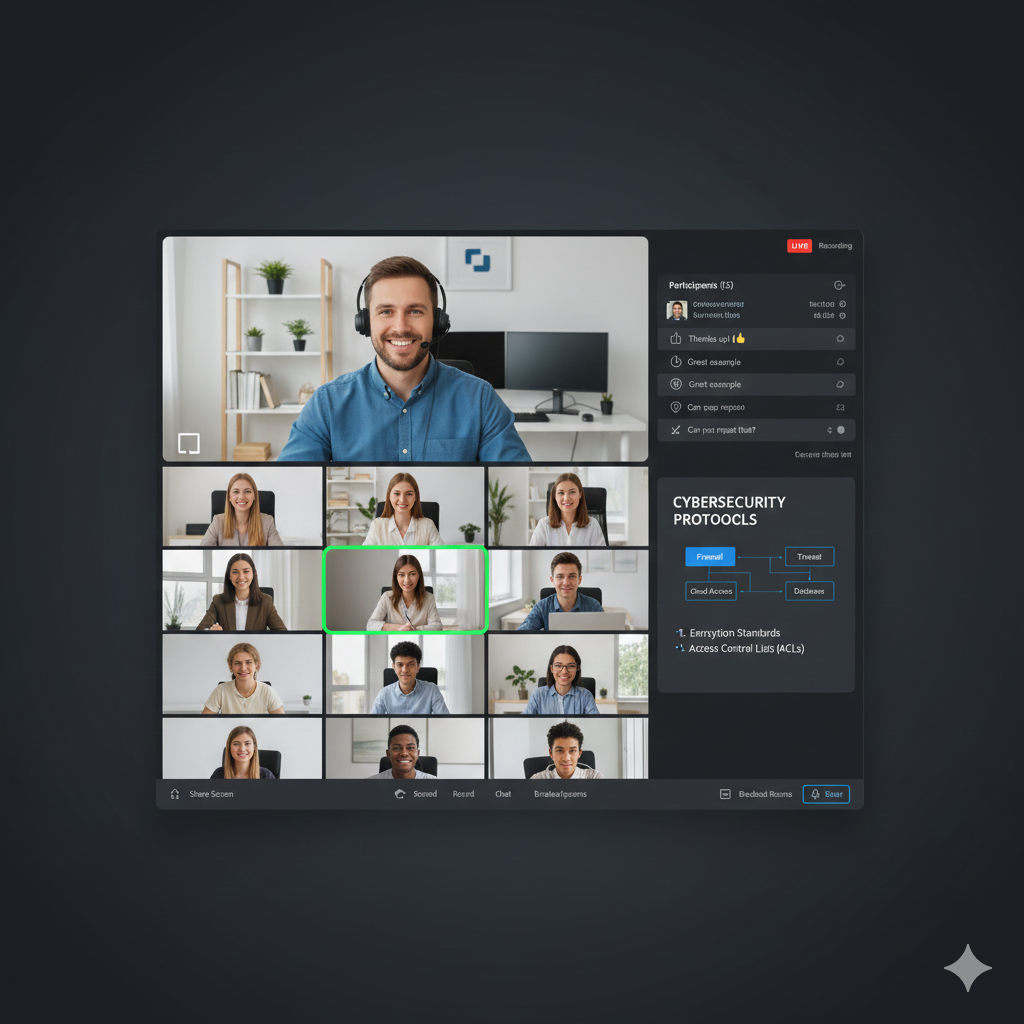
Student attending live online training
B

Live Online

The same instructors and curriculum, delivered live from anywhere on our virtual learning platform.

  • Zero travel required
  • Interactive breakout rooms
Offer

Save on this course with a current special offer

Team pricing, military discounts and a limited-time offer of the week. See what applies before you book.

See special offers
Get Started Today

Explore Your Training Options

Tell us about your training needs and we'll create a personalized plan.

CEH Certification Exam

The Top Ethical Hacking Cert

CEH has 350,000+ holders worldwide and is recognized under DoD 8140, ANAB 17024 and NCSC. Hiring managers look for it.

CEH Exam

All 20 Modules in 5 Days

Recon, scanning, system hacking, malware, web and wireless attacks, cloud, IoT and cryptography, then the 312-50 exam.

CEH Test Exam

AI-Powered Hacking, v13

CEH v13 builds AI into the course: AI-driven recon, attack automation and defense across all five phases of an attack.

CEH Practice Exam

Official EC-Council Content

Authorized CEH v13 materials straight from EC-Council, so you study exactly what the 312-50 exam tests. No guesswork.

CEH Exam Cost

220+ Hands-On Labs

Practice 550+ attack techniques with 4,000+ hacking tools in EC-Council’s iLabs, on real systems with real exploits.

CEH Test Support

Free Exam Retake Included

Your exam voucher, the EC-Council mobile app and post-class instructor access are included, with a free retake if needed.

EC-Council CEH Boot Camp

Accepting Inquiries
+1

    Eligible for Special Pricing?

    We respect your privacy. No spam.

    COURSE STRUCTURE

    CEH Certification Boot Camp
    Syllabus

    A structured path designed for working professionals.
    Each day builds on the last—momentum is everything.

    Request Info

    MODULE_ID: PREP

    Live Training QS: ~5
    BEFORE CLASS
    Critical Path

    Before Class

    Pre-course materials access
    L.prep.1
    Foundation concepts review
    L.prep.2
    Baseline self-assessment
    L.prep.3

    MODULE_ID: CEH-01

    Live Training QS: ~5
    DAY 1
    Critical Path

    Foundations of Ethical Hacking

    Module 1: Introduction to Ethical Hacking
    L.01.1
    Cyber Kill Chain, MITRE ATT&CK, and the Five Hacking Phases
    L.01.2
    Laws, Standards, and AI-Driven Ethical Hacking in CEH v13
    L.01.3
    Module 2: Footprinting and Reconnaissance
    L.01.4
    OSINT With Whois, DNS, Shodan, Maltego, and Google Dorks
    L.01.5
    Lab: Footprinting a Target With Recon-ng and theHarvester
    L.01.6
    Lab: Automating Reconnaissance With AI-Assisted Tools
    L.01.7
    Module 3: Scanning Networks for Hosts and Services
    L.01.8
    Host Discovery, Port Scanning, and OS Fingerprinting With Nmap
    L.01.9
    Scanning Beyond IDS and Firewalls With Hping3 and Decoys
    L.01.10
    Module 4: Enumeration of Users, Shares, and Services
    L.01.11
    NetBIOS, SNMP, LDAP, NFS, SMTP, and DNS Enumeration
    L.01.12
    Enumeration Countermeasures and Service Hardening
    L.01.13
    Lab: Nmap Scanning and Service Version Detection
    L.01.14
    Lab: Enumerating SMB, SNMP, and LDAP Services
    L.01.15

    MODULE_ID: CEH-02

    Live Training QS: ~6
    DAY 2
    Critical Path

    System Hacking and Malware Analysis

    Module 5: Vulnerability Analysis and Assessment Tools
    L.02.1
    Vulnerability Scoring With CVSS, CVE, and NVD
    L.02.2
    Scanning With Nessus and OpenVAS and Reporting Findings
    L.02.3
    Module 6: System Hacking From Access to Persistence
    L.02.4
    Password Cracking With Hashcat and John the Ripper
    L.02.5
    Privilege Escalation, Persistence, Steganography, and Covering Tracks
    L.02.6
    Lab: Vulnerability Scanning and Validation With Nessus
    L.02.7
    Lab: Exploiting a Host With Metasploit and Escalating Privileges
    L.02.8
    Module 7: Malware Threats and Analysis Techniques
    L.02.9
    Trojans, Viruses, Worms, Ransomware, Fileless Malware, and APTs
    L.02.10
    Static and Dynamic Malware Analysis and Countermeasures
    L.02.11
    Module 8: Sniffing Network Traffic and Credentials
    L.02.12
    MAC Flooding, ARP Poisoning, DHCP Starvation, and DNS Poisoning
    L.02.13
    Detecting Sniffers and Hardening Switched Networks
    L.02.14
    Lab: Analyzing Malware Behavior in a Sandbox
    L.02.15
    Lab: ARP Spoofing and Traffic Capture With Wireshark
    L.02.16

    MODULE_ID: CEH-03

    Live Training QS: ~6
    DAY 3
    Critical Path

    Social Engineering, Denial-of-Service, Hijacking, and Evasion

    Module 9: Social Engineering Techniques and Countermeasures
    L.03.1
    Phishing, Vishing, Impersonation, Insider Threats, and Identity Theft
    L.03.2
    AI-Generated Phishing and Deepfake Social Engineering Countermeasures
    L.03.3
    Module 10: Denial-of-Service and DDoS Attacks
    L.03.4
    Volumetric, Protocol, and Application Layer DoS and DDoS Attacks
    L.03.5
    Botnets, Amplification, and DDoS Mitigation Techniques
    L.03.6
    Lab: Building a Phishing Campaign With the Social-Engineer Toolkit
    L.03.7
    Lab: Launching and Detecting SYN Flood Attacks
    L.03.8
    Module 11: Session Hijacking at Network and Application Layers
    L.03.9
    Application and Network Level Hijacking: Session Fixation, MITM, Sidejacking
    L.03.10
    Session Hijacking Countermeasures and Secure Cookie Handling
    L.03.11
    Module 12: Evading IDS, Firewalls, and Honeypots
    L.03.12
    Fragmentation, Obfuscation, Tunneling, and Firewall Evasion Techniques
    L.03.13
    Detecting Honeypots and Hardening IDS and Firewall Deployments
    L.03.14
    Lab: Hijacking a Session With Bettercap and Burp Suite
    L.03.15
    Lab: Evading Snort IDS Rules With Nmap and Packet Crafting
    L.03.16

    MODULE_ID: CEH-04

    Live Training QS: ~7
    DAY 4
    Critical Path

    Web Server, Web Application, SQL Injection, and Wireless Hacking

    Module 13: Hacking Web Servers
    L.04.1
    Web Server Attacks: Directory Traversal, Misconfiguration, and Patch Gaps
    L.04.2
    Module 14: Hacking Web Applications
    L.04.3
    OWASP Top 10: XSS, CSRF, Broken Access Control, and API Attacks
    L.04.4
    Web Application Hacking Methodology and Countermeasures
    L.04.5
    Lab: Attacking a Web Server With Nikto and Metasploit
    L.04.6
    Lab: Exploiting XSS and CSRF With Burp Suite and OWASP ZAP
    L.04.7
    Module 15: SQL Injection Attacks and Defenses
    L.04.8
    Error-Based, Union-Based, Blind, and Out-of-Band SQL Injection
    L.04.9
    SQL Injection Evasion and Defenses With Parameterized Queries
    L.04.10
    Module 16: Hacking Wireless Networks
    L.04.11
    WEP, WPA2, and WPA3 Weaknesses, Evil Twins, and Rogue Access Points
    L.04.12
    Wireless Hacking Countermeasures and Bluetooth Attacks
    L.04.13
    Lab: Exploiting SQL Injection With sqlmap
    L.04.14
    Lab: Cracking WPA2 Handshakes With Aircrack-ng
    L.04.15

    MODULE_ID: CEH-05

    Live Training QS: ~7
    DAY 5
    Critical Path

    Mobile, IoT, Cloud, Cryptography, and Exam Preparation

    Module 17: Hacking Mobile Platforms
    L.05.1
    Android and iOS Attack Vectors, Rooting, Jailbreaking, and MDM Controls
    L.05.2
    Module 18: IoT and OT Hacking
    L.05.3
    IoT and OT Protocols, Modbus, and ICS/SCADA Attack Methodology
    L.05.4
    Module 19: Cloud Computing Threats and Hacking
    L.05.5
    Container, Kubernetes, Serverless, and Cloud Misconfiguration Attacks
    L.05.6
    Lab: Attacking an Android Device With a Malicious APK
    L.05.7
    Lab: Enumerating and Exploiting Misconfigured AWS S3 Buckets
    L.05.8
    Module 20: Cryptography Concepts, PKI, and Attacks
    L.05.9
    Symmetric and Asymmetric Algorithms, Hashing, PKI, and Digital Signatures
    L.05.10
    Cryptanalysis, Disk Encryption, and Cryptographic Attack Countermeasures
    L.05.11
    Lab: Encrypting Data and Attacking Weak Hashes
    L.05.12
    Twenty-Module Review of Tools, Techniques, and Methodologies
    L.05.13
    Nine-Domain Blueprint Review and Question Strategy
    L.05.14
    Full-Length Practice Exam and Review
    L.05.15
    Exam: 312-50
    L.05.16

    MODULE_ID: POST

    Live Training QS: ~8
    AFTER CLASS
    Critical Path

    After Class

    COURSE PROGRESS Day 0 of 5
    DoD Cyber Workforce Framework

    All the CEH Knowledge. Half the Time to Certification.

    Experience accelerated learning to get upskilled, CEH certified, and back to work. Fast.

    Nmap PenetrationTesting CEHv13AI CTF 312-50 SecurityAuditing AIHacking ECCouncil SOCAnalyst CyberDefense WirelessHacking MalwareAnalysis ThreatHunting CEHBootCamp CEHCertification Metasploit NetworkSecurity EthicalHackingSkills PenTestTools DoD8140 Nmap PenetrationTesting CEHv13AI CTF 312-50 SecurityAuditing AIHacking ECCouncil SOCAnalyst CyberDefense WirelessHacking MalwareAnalysis ThreatHunting CEHBootCamp CEHCertification Metasploit NetworkSecurity EthicalHackingSkills PenTestTools DoD8140
    OffensiveSecurity VulnerabilityAssessment CloudSecurity CEH WebAppHacking SocialEngineering CyberSecurity Burpsuite CEHTraining EthicalHacking CertifiedEthicalHacker AICyberSecurity IncidentResponse EthicalHackerCertification RedTeam CEHv13 IoTSecurity KaliLinux SQLInjection Cryptography OffensiveSecurity VulnerabilityAssessment CloudSecurity CEH WebAppHacking SocialEngineering CyberSecurity Burpsuite CEHTraining EthicalHacking CertifiedEthicalHacker AICyberSecurity IncidentResponse EthicalHackerCertification RedTeam CEHv13 IoTSecurity KaliLinux SQLInjection Cryptography
    DoD 8140 Requirements

    Beyond the Cert: Built for the Job

    Foundational qualification The certification you earn with us
    Residential qualification Hands-on labs prep you for the on-the-job readiness DoD 8140 requires within 12 months
    Continuous professional development CPE-eligible training to maintain qualification long after

    The credential, the capability, and the continued readiness — all in one boot camp.

    FREQUENTLY ASKED QUESTIONS

    Official EC-Council CEH
    Boot Camp FAQ

    Real questions from real professionals who passed.
    Here's how we answer them.

    The Certified Ethical Hacker (CEH) v13 is EC-Council’s globally recognized credential for ethical hackers and penetration testers. It validates your ability to identify vulnerabilities, think like an attacker, and defend systems using the same tools and techniques as malicious hackers — now with AI-driven attack and defense integrated throughout all five phases of ethical hacking.

    This course is built for security analysts, SOC analysts, network administrators, IT auditors, and IT professionals moving into offensive security or penetration testing roles. EC-Council recommends at least two years of information security experience, though that requirement is waived when you train with an authorized partner like Training Camp.

    EC-Council requires either completion of official CEH training (which we provide) or two years of verifiable information security work experience plus a $100 eligibility application. Taking our boot camp removes the experience requirement and waives the application fee.

    The CEH knowledge exam is 4 hours long with 125 multiple-choice questions. Passing scores range from 60% to 85% depending on the exam form you receive. You’ll sit the exam at a Pearson VUE testing center or through EC-Council’s remote proctoring service.

    Tuition includes 5 days of live instruction from EC-Council certified trainers, official EC-Council courseware, the CEH 312-50 exam voucher, free retake voucher, EC-Council mobile app access, and 220+ hands-on iLabs.

    CEH v13 integrates AI into all five phases of ethical hacking — reconnaissance, scanning, gaining access, maintaining access, and clearing tracks. It also expands cloud security, IoT and OT hacking, and adds new content on AI-generated malware and deepfake-driven social engineering attacks.

    Yes. CEH is approved under the DoD 8140 Cyber Workforce Qualification Program (the successor to DoD 8570) for multiple cybersecurity work roles, making it a standard requirement for federal and cleared-contractor positions.

    If you don’t pass the CEH exam on your first try, your retake voucher is included at no additional cost. You can also re-attend the boot camp at no charge.

    Get the Free
    CEH Exam Guide

    • Expert strategies to spot trick questions
    • Question patterns examiners actually use
    • Proven pacing + pressure management tactics
    Articles and Certification Resources

    EC-Council CEH
    Study Tools and Resources

    Your journey to EC-Council’s Certified Ethical Hacker (CEH) certification starts with a tailored preparation strategy. We’ve gathered expert insights to guide you every step of the way through the ethical hacking certification process.

    Weighing this against another certification? Compare them head to head in Certification Matchups →

    Student Success Stories

    What Our Students Say

    Join thousands of certified professionals who trained with Training Camp

    ★★★★★

    The Certified Ethical Hacker training program provided by Training Camp was very enjoyable, useful and extremely worthwhile. for our team.

    AC
    Ama*** Car*** A**OM
    ★★★★★

    I would highly recommend the Training Camp CEH experience.

    JW
    Jas** Wit**
    ★★★★★

    The certified ethical hacker solution provided made a real difference for our team success. Top-notch support from start to finish.

    EK
    Edw*** K V**A
    ★★★★★

    Took CISSP and CEH with Training Camp and I owe part of my success to their course and instructor expertise.

    NR
    Nat* Roc** U**Govt
    ★★★★★

    I enjoyed the interaction that the trainer produced through the various Ethical Hacking lab tool activities.

    Free practice test

    Not sure you are ready for the CEH exam yet?

    Our free CEH practice test runs 50 questions on a 90-minute timer, with an explanation for every answer choice, not just the right one. Short on time? Take the 25-question quick version instead.

    Start the CEH test
    Continue Your Journey

    CEH Related Courses

    Advance your career with these recommended certifications

    Featured on