Hello, you are using an old browser that's unsafe and no longer supported. Please consider updating your browser to a newer version, or downloading a modern browser.

Free Practice Test

Free CISSP Practice Test

Check your readiness for the ISC2 Certified Information Systems Security Professional (CISSP) exam with 50 scenario-based questions across all eight domains of the current ISC2 exam outline (effective April 15, 2024), reviewed and updated for 2026, each with an instant explanation. Free to take, timed to the pace of the real exam, and retake it as often as you want.

50Questions, or a 25-question quick test
60 minTimer, paced like the real exam
8CISSP domains covered
A–DEvery answer choice explained, right and wrong

Try a question before you start

Pick an answer to see the reasoning. These are samples from the 59-question bank; the full test starts below.

Security and Risk Management

A risk analyst is evaluating a safeguard for the company's new AI-powered fraud-detection platform. A threat to the platform carries an annual loss expectancy (ALE) of $200,000. A proposed control would reduce the ALE to $50,000 but costs $250,000 per year to operate and maintain. Senior management asks for a recommendation. Which is the MOST defensible recommendation?

Why not A? No premium is given, and blindly transferring regardless of cost is not sound; the transfer cost must still be weighed against the expected loss.

Why not B? A safeguard is justified only when its cost is less than the reduction in expected loss, not for any reduction whatsoever.

Why not D? Reducing ALE by $150,000 while spending $250,000 yields a net loss of $100,000; a desire to show due diligence does not justify a cost-ineffective control.

C is correct. Cost-benefit analysis requires that the safeguard's cost be less than the reduction in ALE; here the control costs more than it saves, so a cheaper mitigation, transfer, or acceptance should be evaluated instead.

Asset Security

While designing a machine-learning pipeline trained on data gathered from external, partly untrusted sources, the security team warns of data poisoning—an adversary injecting mislabeled or crafted samples into the training set to bias the model's behavior. Which control MOST directly mitigates this risk before training begins?

Why not B? Inference-time prompt filtering addresses prompt injection and evasion against an already-trained model; it never sees the training data, which is where poisoning happens.

Why not C? TLS protects queries in transit to the deployed model; it does nothing to stop malicious samples from entering the training pipeline.

Why not D? Access control on the weights prevents theft or tampering after training; poisoning happens earlier, in the data the weights are learned from.

A is correct. Data poisoning corrupts the training set itself, so the control has to act before ingestion: confirm where each external feed comes from and that it arrived unaltered, then screen each incoming batch for outliers, label-distribution shifts and duplicates that signal injected samples. A trusted holdout set, used to compare model behavior after training, adds a second check.

The full test has 50 questions like these. Start it now →

Start Your Free Practice Test

Enter your details, then choose a 25-question Quick Test or the full 50-question, 60-minute practice test.

First Name
Last Name
Phone

A Training Camp advisor may reach out about your results and study options. No spam, and you can opt out anytime.

Prefer to talk to someone?

What you get at the end

Your overall score, a score for each exam domain, and the domains to work on next.

Example report77%
Security and Risk Management83%
Asset Security64%
Security Architecture and Engineering78%
Communication and Network Security71%
Identity and Access Management (IAM)90%
Security Assessment and Testing83%
Security Operations64%
Software Development Security78%
Below 80% is flagged as an area to work on.

What's on the CISSP exam

8 weighted domains. The practice test draws questions from each in the same proportion.

  • 16%

    Security and Risk Management

    Governance, risk analysis, policy, legal and compliance, BCP, and awareness.

  • 10%

    Asset Security

    Data classification, ownership roles, handling, retention, and secure disposal.

  • 13%

    Security Architecture and Engineering

    Secure design principles, security models, cryptography, and physical security.

  • 13%

    Communication and Network Security

    Secure network design, protocols, segmentation, VPNs, and communication channels.

  • 13%

    Identity and Access Management (IAM)

    Authentication, authorization models, federation, and the identity lifecycle.

  • 12%

    Security Assessment and Testing

    Vulnerability assessment, penetration testing, audits, and security metrics.

  • 13%

    Security Operations

    Incident response, forensics, logging and monitoring, change management, recovery.

  • 10%

    Software Development Security

    Secure SDLC, threat modeling, secure coding, and software supply chain controls.

Built on what our boot camp teaches

Every question maps to the same exam objectives we teach in the CISSP boot camp, and every answer choice has its own explanation, so a wrong answer still teaches you something. Questions last reviewed November 11, 2026.

  • Real exam: 100 to 150 questions, delivered as a computerized adaptive test (CAT) in every exam language in 180 minutes (three hours).
  • To pass: a scaled score of 700 on a scale of 1000.
  • This test: 50 questions on a 60-minute timer, or a 25-question quick test.
Read the full CISSP exam guide

This free ISC2 CISSP practice test checks your readiness with 50 scenario-based questions across all eight domains of the current ISC2 exam outline (effective April 15, 2024), each with an explanation for every answer choice. Built by Training Camp, an ISC2 Official Training Partner. New to CISSP? Learn what the certification is and who it is for, or see the accelerated CISSP Certification Boot Camp.

What's on the ISC2 Certified Information Systems Security Professional (CISSP) exam?

CISSP is organized into eight weighted domains under the ISC2 exam outline that took effect April 15, 2024. ISC2 has announced that a new CISSP exam outline takes effect April 15, 2027; if you test before that date, the 2024 blueprint is the one you will sit, so check the official outline if your exam date falls after it. The weightings are listed below, and this practice test pulls questions from every domain in roughly those proportions. For the full breakdown, see our CISSP exam objectives. Domain 1 in particular expects familiarity with governance and risk frameworks such as the NIST Cybersecurity Framework and ISO/IEC 27001.

The exam is a computerized adaptive test (CAT) in every language it is offered in (English, Chinese, German, Japanese and Spanish): you answer between 100 and 150 questions in a three-hour session, and the passing score is 700 out of 1000 points. Questions are written from the point of view of a security manager or architect and ask for the BEST decision, so several of the wrong choices are usually reasonable actions that are simply not the best one. Certification also requires five years of cumulative paid work experience in two or more of the eight domains, one year of which can be waived.

ISC2 refreshes the CISSP outline and question pool on a regular cycle. On April 2, 2026 it published its Exam Guidance for Artificial Intelligence, which maps AI security concepts into the existing domains of every ISC2 exam, including CISSP, rather than adding a new domain. We keep our practice questions aligned with the current published outline and include AI and machine-learning security risks where they map to existing domain objectives.

How to use this practice test

Take all 50 questions once under the 60-minute timer without notes, which is the same pace as the real exam at its 150-question maximum, then read every explanation, including the ones for choices you did not pick. The wrong-answer explanations show the reasoning patterns ISC2 expects: think like a manager, weigh cost against risk, and choose the control that addresses the root problem rather than the symptom. Use the per-domain breakdown to decide where to study, then retake the test after a week to see whether your judgment has shifted. Each attempt draws its 50 questions from a larger pool in the same proportions as the ISC2 domain weights, so a retake brings questions you have not seen.

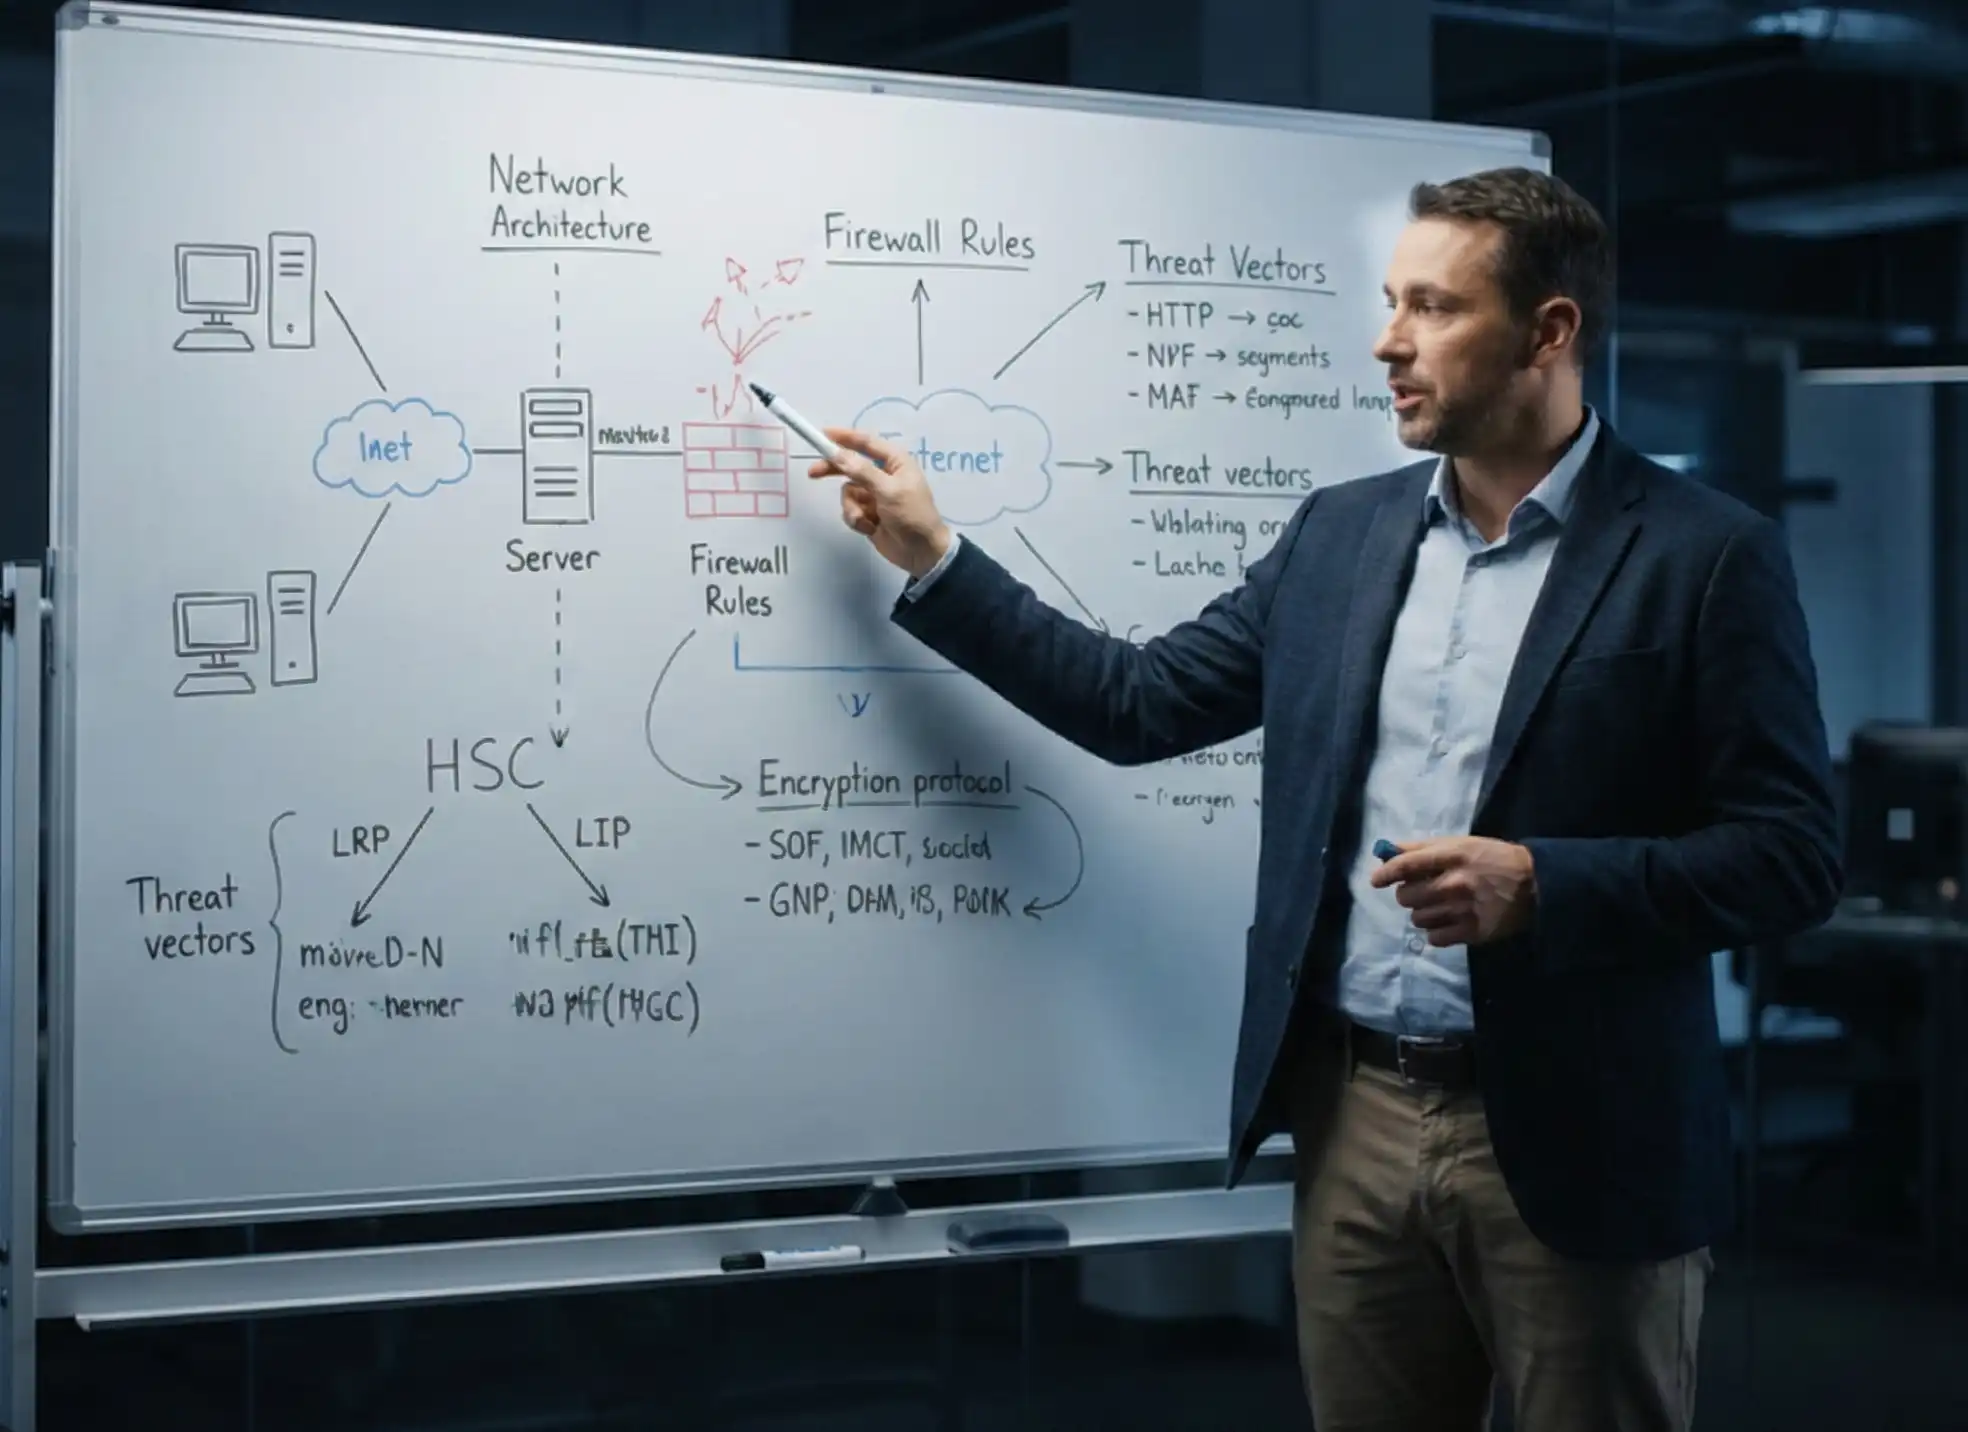
Training Camp instructor teaching network security at a whiteboard

How to get the most from it

Three steps, in this order.

Student working through practice questions at a laptop
Step 1

Take a baseline

Take the full test once without notes, so the score shows where you really stand.

Student reviewing material on a laptop
Step 2

Read every explanation

Including the ones you got right. The notes on the wrong choices explain the differences between similar concepts, like tokenization and encryption.

Students working on laptops in a Training Camp lab
Step 3

Fix one domain, then retake

Your results break down by domain. Study the weakest one for a week, then retake. Each Quick Test draws a fresh mix of questions.

CISSP practice test

Frequently Asked Questions

Quick answers about the test, the ISC2 Certified Information Systems Security Professional (CISSP) exam, and how to prepare.

Is this CISSP practice test free?

Yes. Training Camp's CISSP practice test is completely free, with a written explanation for every answer choice across all eight ISC2 CISSP domains. You can retake it as often as you want.

How does this practice test work?

50 scenario-based questions drawn from all eight CISSP domains, with an instant explanation after each answer and a 60-minute timer, which is timed to the pace of the real exam (up to 150 questions in 180 minutes). Your results break down by domain. Each attempt draws its 50 questions from a larger pool, weighted like the real exam, so you can retake it and see new questions. It is a readiness check, not a substitute for full preparation.

How many questions are on the real CISSP exam?

Since April 15, 2024, every CISSP exam uses Computerized Adaptive Testing (CAT) with 100 to 150 questions and a three-hour time limit, in all five exam languages. Because the exam adapts to your answers, the exact number of questions varies from one candidate to the next.

What score do I need to pass CISSP?

You need a scaled score of 700 on a scale of 1000 to pass the CISSP exam. The scaled score is not a percentage of questions answered correctly.

What domains does the CISSP exam cover?

The current exam outline, effective April 15, 2024, has eight domains: Security and Risk Management (16%), Asset Security (10%), Security Architecture and Engineering (13%), Communication and Network Security (13%), Identity and Access Management (IAM) (13%), Security Assessment and Testing (12%), Security Operations (13%), and Software Development Security (10%).

What experience do I need to become CISSP certified?

You can sit the exam at any time, but to certify ISC2 requires five years of cumulative paid work experience in two or more of the eight domains. One year can be waived with a qualifying four-year degree or an approved credential, and candidates who pass without the full experience become an Associate of ISC2 while they earn it.

How hard is the CISSP exam?

CISSP is an advanced exam aimed at experienced practitioners. It rewards management-level judgment and breadth across the whole security program: most questions describe a situation and ask for the BEST decision, and several of the wrong choices are usually reasonable. Candidates with hands-on experience across several domains tend to find the reasoning familiar; others need to practice thinking like a manager rather than a technician.

How should you prepare for the CISSP exam?

Work through the official CISSP exam outline, use a structured CISSP study guide, and consider an accelerated CISSP Certification Boot Camp that includes the exam voucher and a free retake if you need it. Practice questions help you get used to the exam's think-like-a-manager framing.

Need CISSP for a DoD role?

For a lot of people this test is the first step toward a DoD 8140 requirement or a military-to-civilian move.

  • DoD 8140: The CISSP appears in the DoD 8140 Qualification Matrix across 11 work roles and qualifies at the Advanced proficiency level in every one of them. How 8140 qualification works →
  • Post-9/11 GI Bill®: our live online CISSP Certification Exam Preparatory Course is approved for Chapter 33 benefits, and the VA can reimburse the exam fee as well. See the GI Bill® prep course →
U.S. Army service member working on a laptop
Instructor-led Training Camp class

Ready to pass it for real?

The CISSP boot camp covers every exam domain with a live instructor, online or in person.

  • Exam voucher included
  • Free retake
  • 180 days of unlimited 1-on-1 coaching after class