Hello, you are using an old browser that's unsafe and no longer supported. Please consider updating your browser to a newer version, or downloading a modern browser.

Free Practice Test

Free PenTest+ Practice Test
for PT0-003

Check your readiness for the CompTIA PenTest+ (PT0-003) exam with 50 exam-style questions across all five domains, each with an instant explanation. Free to take, with a 90-minute timer that matches the pace of the real exam, and retake it as often as you want.

50Questions, or a 25-question quick test
90 minTimer, paced like the real exam
5PT0-003 domains covered
A–DEvery answer choice explained, right and wrong

Try a question before you start

Pick an answer to see the reasoning. These are samples from the 50-question bank; the full test starts below.

Engagement Management

A client requires that one legacy system never be tested during an authorized assessment. Which of the following sections of the rules of engagement records this requirement?

Why not A? The testing window defines the dates and hours when testing may take place. It does not remove a system from scope.

Why not B? The escalation process names who the tester contacts when a problem arises, such as an outage. It does not define what is out of scope.

Why not D? Test cases describe what the tester will attempt against in-scope systems. They do not remove systems from the engagement.

C is correct. Exclusions in the rules of engagement list the systems, addresses or techniques that are off limits for the engagement. A system that must never be tested is recorded there.

Reconnaissance and Enumeration

A tester reviews an authorized target's certificate transparency logs and public DNS records without sending any packets to the client's systems. Which of the following BEST describes this activity?

Why not B? Active reconnaissance sends probes such as port scans directly to the target, which the target can log and detect.

Why not C? Authenticated scanning logs in to a system with valid credentials to inspect it from the inside, which is highly interactive rather than passive.

Why not D? Protocol fuzzing sends malformed input to a service to find flaws. It is an active testing technique, not information gathering from public sources.

A is correct. Passive reconnaissance gathers information from public sources such as search engines, DNS records and certificate transparency logs, so the target never sees traffic from the tester.

The full test has 50 questions like these. Start it now →

Start Your Free Practice Test

Enter your details, then choose a 25-question Quick Test or the full 50-question, 90-minute practice test.

First Name
Last Name
Phone

A Training Camp advisor may reach out about your results and study options. No spam, and you can opt out anytime.

Prefer to talk to someone?

What you get at the end

Your overall score, a score for each exam domain, and the domains to work on next.

Example report77%
Engagement Management83%
Reconnaissance and Enumeration64%
Vulnerability Discovery and Analysis78%
Attacks and Exploits71%
Post-exploitation and Lateral Movement90%
Below 80% is flagged as an area to work on.

What's on the PT0-003 exam

5 weighted domains. The practice test draws questions from each in the same proportion.

  • 13%

    Engagement Management

    Scoping, rules of engagement, agreements, methodologies, reporting, and remediation guidance.

  • 21%

    Reconnaissance and Enumeration

    Passive and active recon, OSINT, DNS, enumeration techniques, scripting, and the right tools.

  • 17%

    Vulnerability Discovery and Analysis

    Scan types, authenticated scanning, output analysis, exploit selection, and physical security.

  • 35%

    Attacks and Exploits

    Network, authentication, host, web, cloud, wireless, social engineering, and specialized attacks.

  • 14%

    Post-exploitation and Lateral Movement

    Persistence, lateral movement, pivoting, staging and exfiltration, and cleanup.

Built on what our boot camp teaches

Every question maps to the same exam objectives we teach in the PenTest+ boot camp, and every answer choice has its own explanation, so a wrong answer still teaches you something. Questions last reviewed September 29, 2026.

  • Real exam: a maximum of 90 questions in 165 minutes.
  • To pass: a scaled score of 750 on a scale of 100 to 900.
  • This test: 50 questions on a 90-minute timer, or a 25-question quick test.
Read the full PenTest+ exam guide

This free CompTIA PenTest+ practice test checks your readiness for the PT0-003 exam with 50 exam-style questions across all five domains, each with an explanation for every answer choice, on a 90-minute timer. Built by Training Camp and drawn from the same objectives we teach in our CompTIA PenTest+ Boot Camp. If you are new to the certification, start with what is PenTest+.

What's on the CompTIA PenTest+ (PT0-003) exam?

The PT0-003 exam has five weighted domains: Engagement Management (13%), Reconnaissance and Enumeration (21%), Vulnerability Discovery and Analysis (17%), Attacks and Exploits (35%), and Post-exploitation and Lateral Movement (14%). You get 165 minutes for a maximum of 90 questions, which are a mix of multiple choice and performance-based items, and you need a scaled score of 750 on a scale of 100 to 900 to pass. PT0-003 is the current version, launched in December 2024.

PenTest+ sits at the intermediate level. There are no formal prerequisites, but CompTIA recommends Network+ and Security+ or equivalent knowledge along with three to four years of hands-on penetration testing or related experience. The certification is valid for three years and can be renewed through continuing education.

How to use this practice test

Take it once without notes to get an honest baseline, then read the explanation for every answer, including the ones you got right. The incorrect-choice explanations are where the distinctions the exam likes to test (SAST versus DAST, pass-the-hash versus pass-the-ticket, CVSS versus EPSS) get spelled out. Study your weakest domain and retake the test in a week. Every scenario here is framed as an authorized engagement with a signed scope, which mirrors how the exam expects you to think: the rules of engagement come first, and the right next step is always the one that stays inside scope.

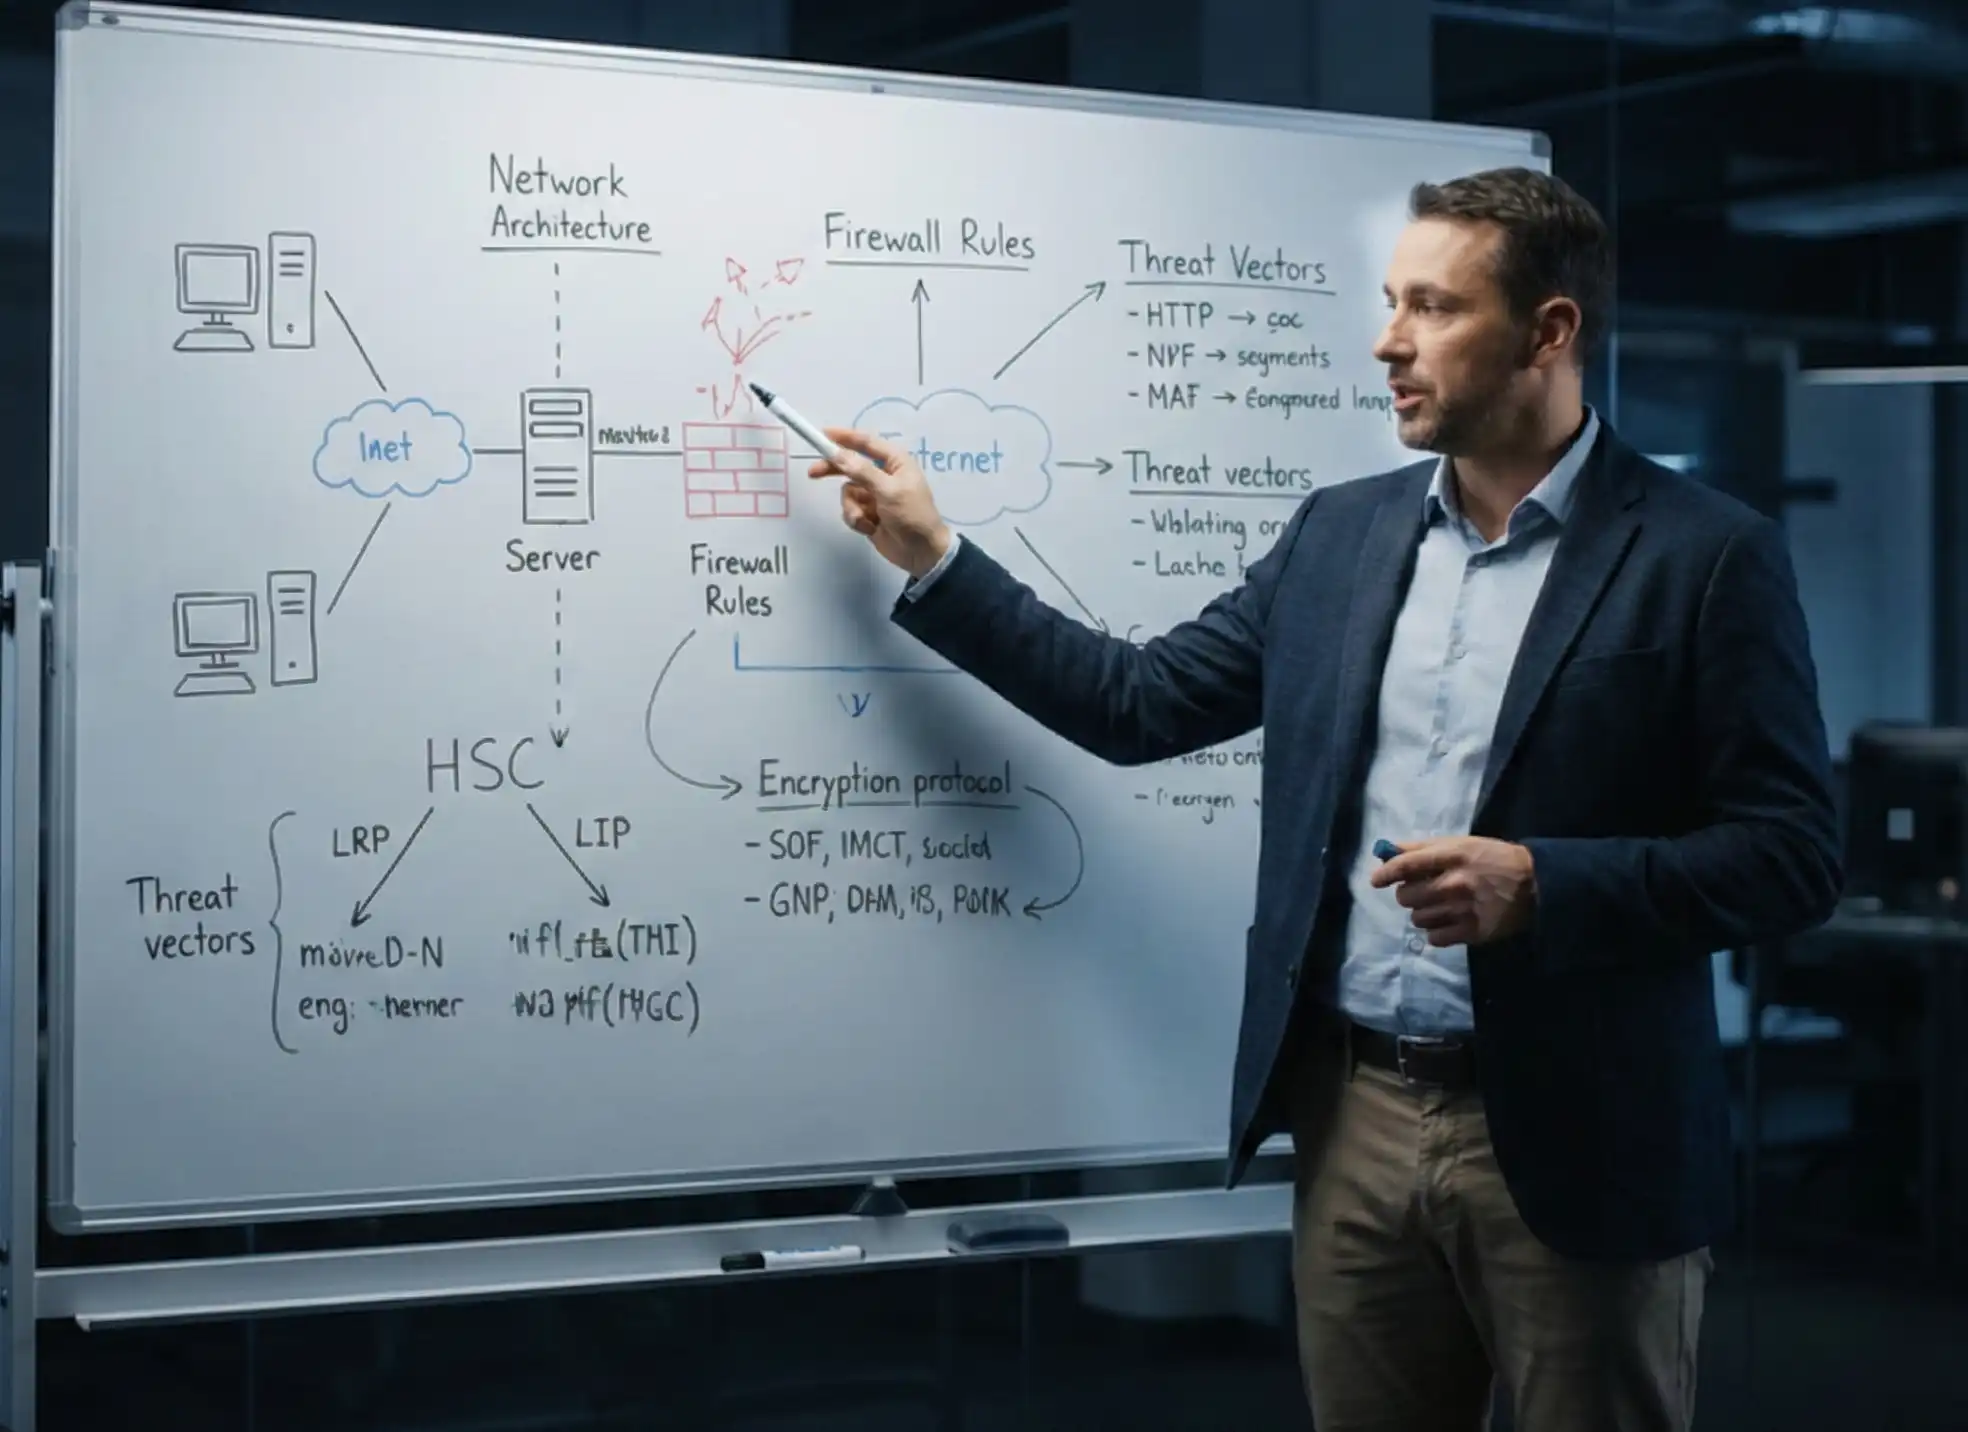
Training Camp instructor teaching network security at a whiteboard

How to get the most from it

Three steps, in this order.

Student working through practice questions at a laptop
Step 1

Take a baseline

Take the full test once without notes, so the score shows where you really stand.

Student reviewing material on a laptop
Step 2

Read every explanation

Including the ones you got right. The notes on the wrong choices explain the differences between similar concepts, like tokenization and encryption.

Students working on laptops in a Training Camp lab
Step 3

Fix one domain, then retake

Your results break down by domain. Study the weakest one for a week, then retake. Each Quick Test draws a fresh mix of questions.

PenTest+ Practice Test

Frequently Asked Questions

Quick answers about the test, the CompTIA PenTest+ (PT0-003) exam, and how to prepare.

Is this CompTIA PenTest+ practice test free?

Yes. Training Camp's CompTIA PenTest+ (PT0-003) practice test is free to take. You get 50 exam-style questions across all five domains, with a written explanation for every answer choice.

How does this practice test work?

It is 50 multiple-choice scenario questions drawn from all five PT0-003 domains, with an instant explanation after each answer and a 90-minute timer. You can retake it as often as you want. Treat it as a readiness check rather than a substitute for full preparation.

How many questions are on the real CompTIA PenTest+ exam?

The PT0-003 exam has a maximum of 90 questions and gives you 165 minutes. The questions are a mix of multiple choice and performance-based items, where you complete a hands-on style task rather than pick a single answer.

What score do I need to pass the CompTIA PenTest+ exam?

You need a scaled score of 750 on a scale of 100 to 900. CompTIA reports one overall scaled score, so a strong domain can offset a weaker one. There is no separate bar to clear in each domain.

What domains does the CompTIA PenTest+ exam cover?

The five domains are Engagement Management (13%), Reconnaissance and Enumeration (21%), Vulnerability Discovery and Analysis (17%), Attacks and Exploits (35%), and Post-exploitation and Lateral Movement (14%). Attacks and Exploits is the largest, so most of your study time belongs there.

Do I need experience to take the CompTIA PenTest+ exam?

There are no formal prerequisites. CompTIA recommends CompTIA Network+ and CompTIA Security+ or equivalent knowledge along with three to four years of hands-on penetration testing or related experience, which makes it an intermediate rather than an entry-level certification.

How long is the CompTIA PenTest+ certification valid?

PenTest+ is valid for three years from the date you pass. You renew it through CompTIA's continuing education program, by earning credits or a higher-level certification, rather than by retaking the exam.

How should you prepare for the CompTIA PenTest+ exam?

Start with the PT0-003 exam objectives and learn each attack, tool and reporting step at the level the objectives name, then use practice questions like these to find your weak domains. If you want a structured path with an instructor and hands-on labs, our CompTIA PenTest+ Boot Camp covers all five domains.

Instructor-led Training Camp class

Ready to pass it for real?

The PenTest+ boot camp covers every exam domain with a live instructor, online or in person.

  • Exam voucher included
  • Free retake
  • 180 days of unlimited 1-on-1 coaching after class