
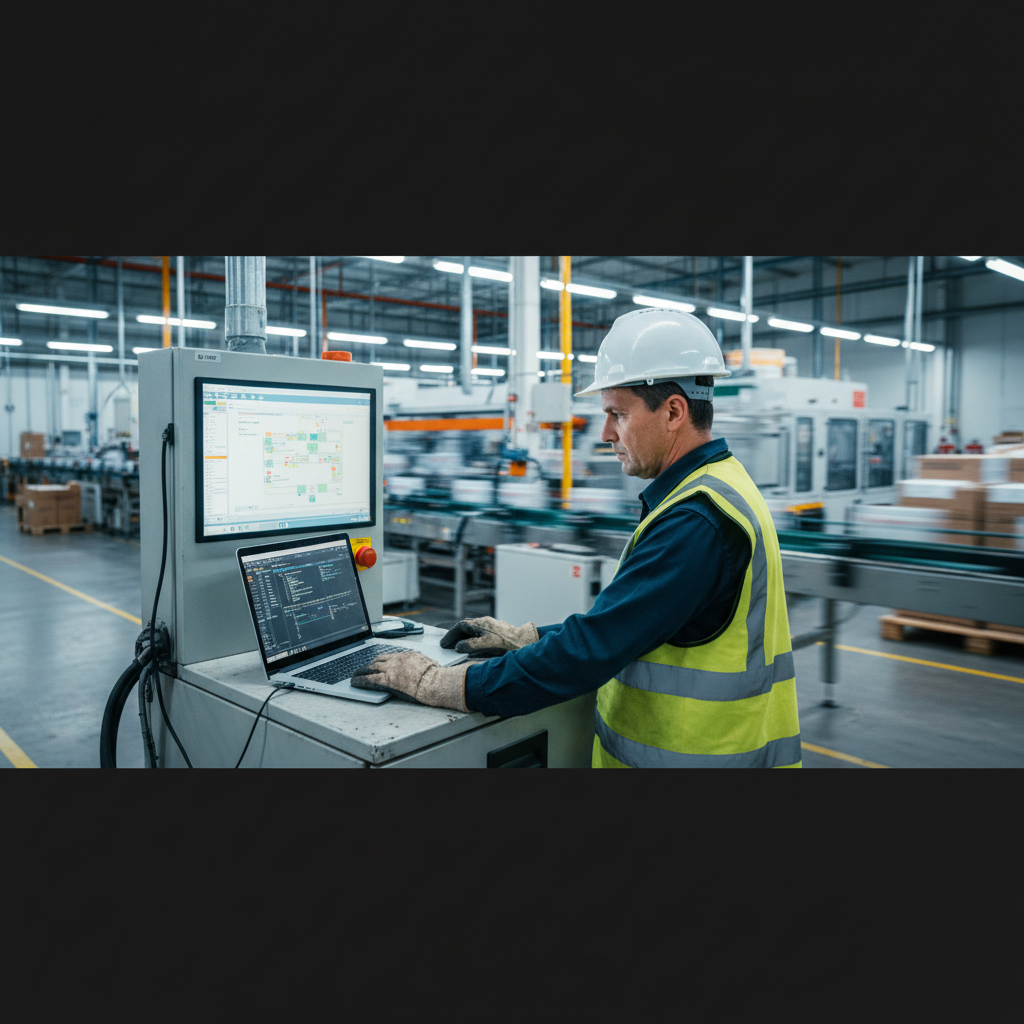
Patch Tuesday does not exist on a factory floor. A programmable logic controller running a bottling line might go five years between firmware updates, not because anyone forgot, but because stopping the line costs more per hour than the unpatched vulnerability is likely to cost per year. Every habit an IT security person brings to that environment, patch fast, scan everything, reboot if in doubt, has to be re-examined against that tradeoff. That re-examination is the real subject of CompTIA SecOT+, the company’s first certification focused entirely on operational technology security, and it is what makes the exam harder for experienced IT people than the question count suggests.
SecOT+ (exam SOT-001) launches in December 2026 and is open for preorder now. This guide covers what the exam tests, where the six domains overlap with what a Security+ or CySA+ holder already knows, where they do not, and how to study the parts that are new. For the quick overview of launch dates and pricing, the SecOT+ summary page on this site has the short version. This piece is the longer one about how to learn the material.
SecOT+ is 95 questions in 90 minutes, passing score 750 out of 900, across six OT domains. The biggest domain is OT Security Operations at 22 percent, and the concept that runs under all six is that safety and availability come before confidentiality in a plant.
Preparing for the Security+ exam? Compare class dates and formats for our Security+ boot camp.
What is CompTIA SecOT+?
CompTIA SecOT+ is a vendor neutral certification for securing operational technology: the programmable logic controllers, human machine interfaces, remote terminal units, historians and industrial networks that run manufacturing plants, power grids, water utilities, and oil and gas operations. Announced in May 2025 and run as a beta through the summer of 2026, it is described by CompTIA as the first of its certifications focused exclusively on OT security. The exam is performance based, which means some questions ask you to do something in a simulated environment rather than pick an answer from a list.
| Exam fact | SecOT+ V1 (SOT-001) |
|---|---|
| Questions | Up to 95, multiple choice and performance based |
| Time | 90 minutes |
| Passing score | 750 on a scale of 100 to 900 |
| Launch | December 2026 (CompTIA’s page lists both December 1 and on or around December 8) |
| Prerequisites | None required. CompTIA recommends 3 or more years of hands on OT experience and 2 or more years implementing OT security |
| Language | English at launch |
| Retirement | Estimated three years after launch |
| Renewal | Three year CE cycle. CEU count and fee not yet published |
| Accreditation | Listed as TBD in the objectives |
Two of those rows deserve a note. The launch date conflict is on CompTIA’s own certification page, which says December 1 in the exam details section and on or around December 8 in the overview, so plan around the second week of December rather than the first. And the recommended experience is steeper than the entry level number of questions implies. Three years hands on in OT describes a working practitioner. CompTIA does not enforce it, but the objectives are written to it.
How is OT security different from IT security?
Start with the one idea that reorganizes everything else. In IT security you learned confidentiality, integrity and availability in that order, and most of your controls protect data. OT flips that order. Safety comes first, because a control system that does the wrong thing can injure a person. Then availability, since the process cannot stop. Confidentiality lands a distant third, because the data moving between a controller and a valve is a number on a wire that nobody needs to keep secret.
Think of the difference between an office building and a hospital ward. In the office, if a server is misbehaving you shut it down and sort it out. On the ward, a misbehaving ventilator is attached to a patient, and the first question is not how to fix it but how to keep the patient breathing while you figure out what is wrong. OT security is the hospital ward. Every control you apply has to be checked against whether it could trip the process, and the people who own the process will veto it if it can.
That single flip explains most of what feels strange to an IT person reading the SecOT+ objectives. Active vulnerability scanning can crash a PLC, so asset discovery in OT is usually passive, listening to traffic rather than probing devices. Patching waits for a planned outage window, which might be once a year, so vulnerability management is about compensating controls and risk acceptance rather than remediation speed. The industrial protocols, Modbus, DNP3, EtherNet/IP, Profinet, were designed decades ago for reliability on isolated networks and most of them have no authentication at all, so segmentation does the work that identity does in IT. And the operating systems are old because the vendor certified the control software against that specific version and will not support a newer one. None of this is negligence. The constraints are different, and the exam tests whether you can reason inside them.
Study tip: Build a two column table as you read the objectives. Left column, the IT control you already know: patching, network scanning, MFA, EDR, incident response. Right column, what replaces or modifies it in OT: planned outage windows, passive discovery, jump hosts with privileged access management, OT aware IDS, incident response that prioritizes loss of safety over loss of data. Most SecOT+ questions are written at the seam between those two columns, and a candidate who can explain why the right column exists will reason through scenarios they have never seen.
What are the SecOT+ exam domains?
The objectives document, version 2.1, lists six domains, and the weights below are CompTIA’s. My notes on each are about where an IT security background carries you and where it stops.
Add it up by familiarity. Domains 2, 3 and 6, which total 46 percent, build on frameworks an IT security person already uses, with OT specific adjustments. The other three, domains 1, 4 and 5 at 54 percent, are where the new material lives: the devices, the protocols, the segmentation model and the operating constraints. That is the split to plan a study calendar around, and it is backwards from how most people instinctively study, which is to start with what they know.
Who should take SecOT+?
CompTIA names the target roles as OT security engineer or specialist, ICS and SCADA security engineer, OT security architect, critical infrastructure engineer, and site or plant OT lead. Its 2025 announcement also pointed at floor technicians, industrial engineers and network architects, which is a wider net, and it cited more than 180,000 U.S. job postings in 2024 that called for OT skills. The honest reading of those two lists together is that SecOT+ is aimed at two groups coming from opposite directions: security people who need to learn the plant, and plant people who need to learn security.
For the security side, the sensible entry point is someone who holds Security+ and has worked in a SOC or on a network team, and who is now being asked about the manufacturing network, the building management system or the utility’s control center. If that is you, the guide to what comes after Security+ now has one more branch. SecOT+ is a specialization, so on that map it sits beside CySA+ rather than above it. The comparison in SecAI+ vs CySA+ applies the same logic to CompTIA’s other new specialization.
For the plant side, an engineer or technician who already understands the process and the equipment has the harder half of the exam covered and needs to learn the security frameworks, the threat intelligence models and the incident response structure. That person usually finds domains 2, 3 and 6 to be the study load, which is the mirror image of the IT candidate.
One group should wait. If you have never worked in a SOC, never read a packet capture and never done a risk assessment, SecOT+ assumes too much. The objectives recommend two years implementing OT security, and the questions are written for someone who has made the tradeoffs the exam asks about. Security+ first, then time on a network or security team, then SecOT+ when an OT environment is actually in front of you.
When does SecOT+ launch and what does it cost?
The exam launches in December 2026. CompTIA’s page gives December 1 in one place and on or around December 8 in another. Preorders are open now through the SecOT+ certification page, with access delivered through your CompTIA account at launch and a refund only if the launch slips more than three months. CompTIA has not posted a price on the certification page. The U.S. store lists the voucher at about $439, which lines up with the May 2026 increase that took Security+, CySA+ and PenTest+ from $425 to $439, but confirm it in the store before you buy.
Renewal follows CompTIA’s three year continuing education cycle, but the CEU count and fee for SecOT+ have not been published. For scale, SecAI+ requires 15 CEUs and $75 over three years, and Security+ requires 50 CEUs and $150. Accreditation is listed as TBD in the objectives. CompTIA’s pattern with SecAI+, which launched in February 2026 and earned ANAB accreditation the same year, suggests SecOT+ will follow, and ANAB accreditation is the first gate for appearing in the DoD 8140 qualification matrices. Until that happens, SecOT+ does not satisfy any DCWF work role, and the eight CompTIA certifications that currently do are listed in the DCWF work role map.
How to study for SecOT+
Read the objectives document first, all of it, and mark every term you cannot define. The method for turning an objectives document into a study plan works the same way here, with one adjustment: for SecOT+ the unknown terms cluster in domain 1, and they are physical things. A VFD is a variable frequency drive that controls a motor’s speed. An IED is an intelligent electronic device in a substation. A historian is a database that stores process values over time. You cannot reason about securing a device you cannot picture, so spend the first week on what the equipment does before you read a word about threats.
Then read the two documents the objectives point at. NIST SP 800-82 Revision 3, the Guide to Operational Technology Security, was published in September 2023 and a Revision 4 draft is out for comment. It is long, but sections 2 through 5 are the plain language explanation of OT architecture and risk that the exam assumes. The ISA/IEC 62443 series is the source of the zones and conduits model and the security level concept in domain 4. You do not need to buy the standards. The ISA overview and the terminology are enough for the exam, and the 62443 certificate program is the main alternative credential if you later want to go deeper on that one framework.
For domain 3, work through the MITRE ATT&CK for ICS matrix and then read a short account of each named incident. Stuxnet is the PLC logic manipulation case. BlackEnergy and Industroyer are the Ukrainian grid attacks of 2015 and 2016. TRISIS targeted a safety instrumented system. FrostyGoop used Modbus directly against heating controllers. Colonial Pipeline was an IT ransomware event that shut down OT as a precaution. Knowing which technique category each one demonstrates matters more than the dates, because the exam uses them as reference cases for scenario questions. Then map two of them onto the ICS Cyber Kill Chain yourself, stage by stage. That exercise turns a list of names into a model you can apply to an incident you have not read about.
For domains 4 and 5, get hands on with traffic. Capture or download a Modbus TCP packet capture and open it in Wireshark. Find the function codes, the unit identifier and the register addresses, and notice that there is no authentication field anywhere in the frame. That one observation makes segmentation, data diodes and the industrial DMZ stop being abstractions. The same habits that make reading security logs a learnable skill apply to industrial protocols. You are looking for what normal looks like first, then for the deviation.
Study tip: Practice the performance based questions by writing out, in order, what you would do in three scenarios: a new unknown device appears on the control network, a vendor needs remote access to a PLC during production, and a workstation on the plant floor shows ransomware. For each one, write the IT instinct first, then cross out every step that could stop the process or trip a safety system, then write what replaces it. That editing step is the exam.
Frequently Asked Questions
What is the CompTIA SecOT+ exam code?
The exam code is SOT-001, version 1. During the 2026 beta the code was SO1-001. Both refer to the same certification, and only SOT-001 will be available after launch.
How many questions are on the SecOT+ exam?
Up to 95 questions in 90 minutes, including multiple choice and performance based items. The passing score is 750 on CompTIA’s 100 to 900 scale.
When does SecOT+ launch?
December 2026. CompTIA’s certification page lists December 1 in the exam details and on or around December 8 in the overview. Preorders are open now, and access is delivered through your CompTIA account at launch.
Does SecOT+ have prerequisites?
No required prerequisites. CompTIA recommends three or more years of hands on OT experience and two or more years implementing OT cybersecurity. Security+ is not listed as a prerequisite, but the objectives assume you already understand core security controls and incident response.
What are the SecOT+ domains?
Six domains: OT Systems and Safety Foundations (14%), OT Risk Management (17%), OT Threat Intelligence (14%), OT Cybersecurity Architecture, Design and Engineering (18%), OT Security Operations (22%), and OT Incident Management (15%).
Is SecOT+ approved for DoD 8140?
Not yet. The objectives list accreditation as TBD, and ANAB accreditation is the first requirement for inclusion in the DoD 8140 qualification matrices. CompTIA’s SecAI+ earned ANAB accreditation within its launch year, so SecOT+ may follow, but as of October 2026 it does not satisfy any DCWF work role.
How much does SecOT+ cost?
CompTIA has not posted a price on the certification page. The U.S. store lists the exam voucher at about $439 as of October 2026, in line with CompTIA’s other core security exams after the May 2026 price change. Confirm the current price in the store before purchasing.
VP of Educational Services | Training Camp
Jeff Porch is the VP of Educational Services and Operations at Training Camp, where he leads the company's educational initiatives with a focus on accelerated learning and student success. Beyond overseeing curriculum development, Jeff serves as the lead course designer for Training Camp's CompTIA Security+ program, one of their most popular offerings. He is deeply involved in the instructional side of the business — developing certification courses, training instructors, and ensuring that complex IT concepts are delivered in ways that maximize retention and minimize time-to-certification.